Published Sunday, October 04, 2026 at 04:27 PM PT

BLUF: Internal IPS detected aggressive port scanning from 192.168.1.9 to 192.168.1.138 (5 ports in 60 seconds) on 2026-10-04. This is a lateral movement pattern consistent with post-compromise reconnaissance. Immediate action: isolate source IP 192.168.1.9 pending asset identification and forensics. Scope limited to internal network; external entry vector unknown.
DETAILS
- IPS alert triggered on nova-core: 192.168.1.9 scanned 5 distinct ports on 192.168.1.138 within 60-second window — scanning rate and density consistent with active compromise or lateral movement staging.
- Traffic is internal (RFC 1918 addresses); no external component observed in available telemetry.
- Target ports not specified in alert; recommend immediate retrieval of flow data to identify which services were probed.
- Source asset 192.168.1.9 identity unknown — may be compromised workstation, rogue VM, or attacker pivot point from initial breach.
- Alert status: Detected only — no confirmation of successful exploitation or data exfiltration at this time.
IMPACT
- Scope: Internal network segment containing 192.168.1.0/24.
- Affected systems: 192.168.1.138 (target) and 192.168.1.9 (source). Assets beyond these two not yet confirmed compromised.
- Risk level: HIGH — lateral movement is post-compromise activity; implies attacker already has network access and is mapping internal topology.
RECOMMENDED ACTIONS
- Immediate: Isolate 192.168.1.9 from network pending forensics (preserve for analysis, do not wipe).
- Immediate: Pull full IPS logs for port details and check for success/failure indicators on 192.168.1.138.
- Within 1 hour: Identify both assets (MAC addresses, asset register, DHCP logs); determine if either is expected or rogue.
- Within 2 hours: Check 192.168.1.138 for intrusion artifacts (failed connection attempts, successful logins, privilege escalation).
- Ongoing: Expand search for other lateral scans from same source IP or similar patterns; check for initial compromise vector (phishing, VPN, unpatched exposure).
SOURCES
- IPS alert from nova-core (detection engine: lateral_movement; timestamp: 2026-10-04; action: detected)
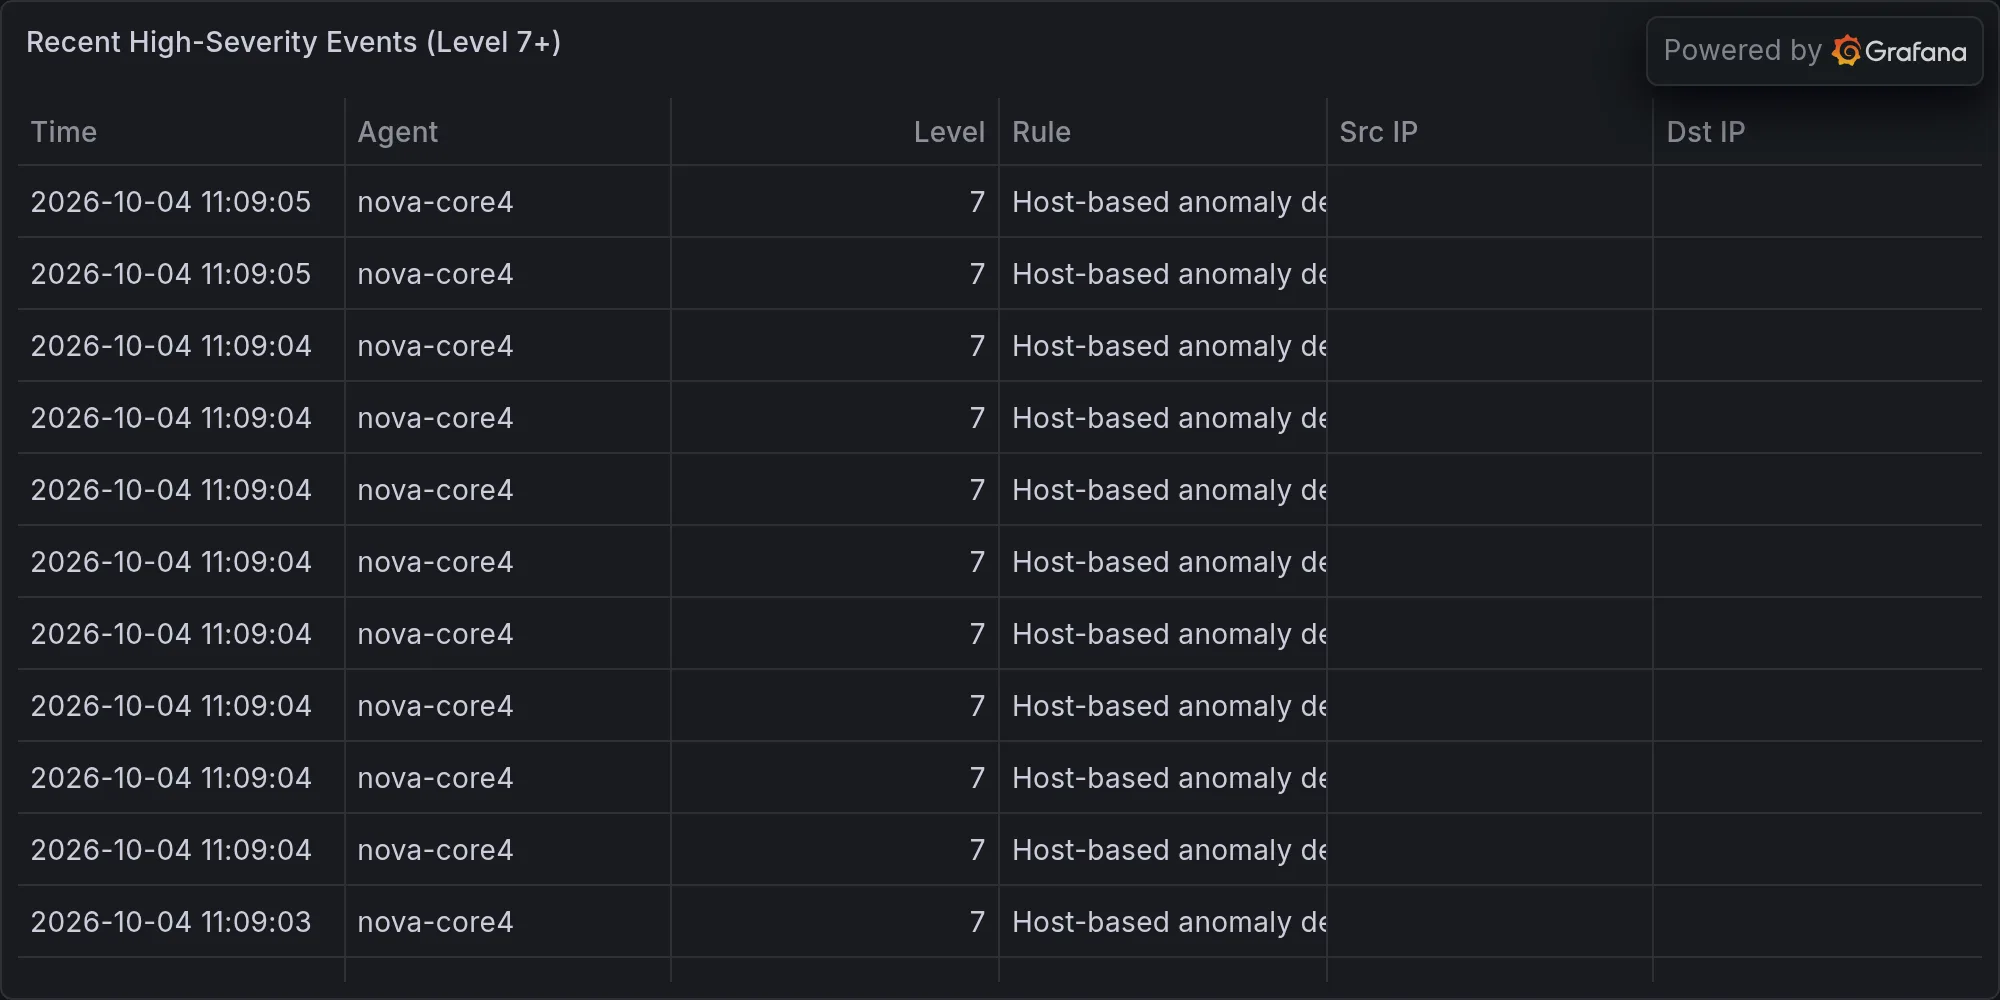
Recent high-severity events at publish time: