Published Sunday, October 04, 2026 at 11:54 AM PT

BLUF: IPS on nova-core detected rapid multi-port reconnaissance from internal host 192.168.1.9 scanning 5 ports on target 192.168.1.138 within 60 seconds. This is lateral movement activity characteristic of internal reconnaissance preceding exploitation. Source and target identities and intent currently unconfirmed. Immediate host identification and network isolation recommended.
DETAILS
- Detection: IPS rule triggered on nova-core network; threat classification:
lateral_movement, action:detected(status of block/allow not provided) - Attack pattern: 5 distinct ports scanned on target within 60-second window. Specific ports not provided. Scan rate suggests automated reconnaissance tools
- Network scope: Both source (192.168.1.9) and target (192.168.1.138) are internal RFC 1918 addresses on same network segment
- Detection method: Signature-based IPS threshold rule; confidence level of detection: presumed high (rule fired), confidence of attribution/intent: low (no payload analysis provided)
- Timeline: Single 60-second event window; no indication of sustained scanning or follow-up activity
IMPACT
- Primary: Target host 192.168.1.138 — role and criticality unknown, cannot assess exploitation risk without device identification
- Secondary: If source (192.168.1.9) is compromised, lateral movement may continue to other internal segments
- Scope: Internal network only; no external C2 or internet-origin indicators in alert
- Known unknowns: Port identities, payload content (if any), whether traffic was blocked by firewall, source device ownership
RECOMMENDED ACTIONS
- Identify both hosts immediately — What is 192.168.1.9? What is 192.168.1.138? Confirm ownership, OS, running services
- Extract full IPS logs — Port numbers, packet counts, any payloads, full timestamp
- Check target (192.168.1.138) for service vulnerabilities, listening ports, and failed login/exploit attempts in last 24h
- Verify source (192.168.1.9) — Confirm it is a legitimate device; pull process logs, network activity history, user login records
- If target is critical infrastructure, isolate it from network pending verification
- Escalate to security ops — Do not assume benign without device ownership confirmation
SOURCES
IPS alert: nova-core lateral_movement rule | Detection confidence: HIGH | Attribution confidence: UNCONFIRMED
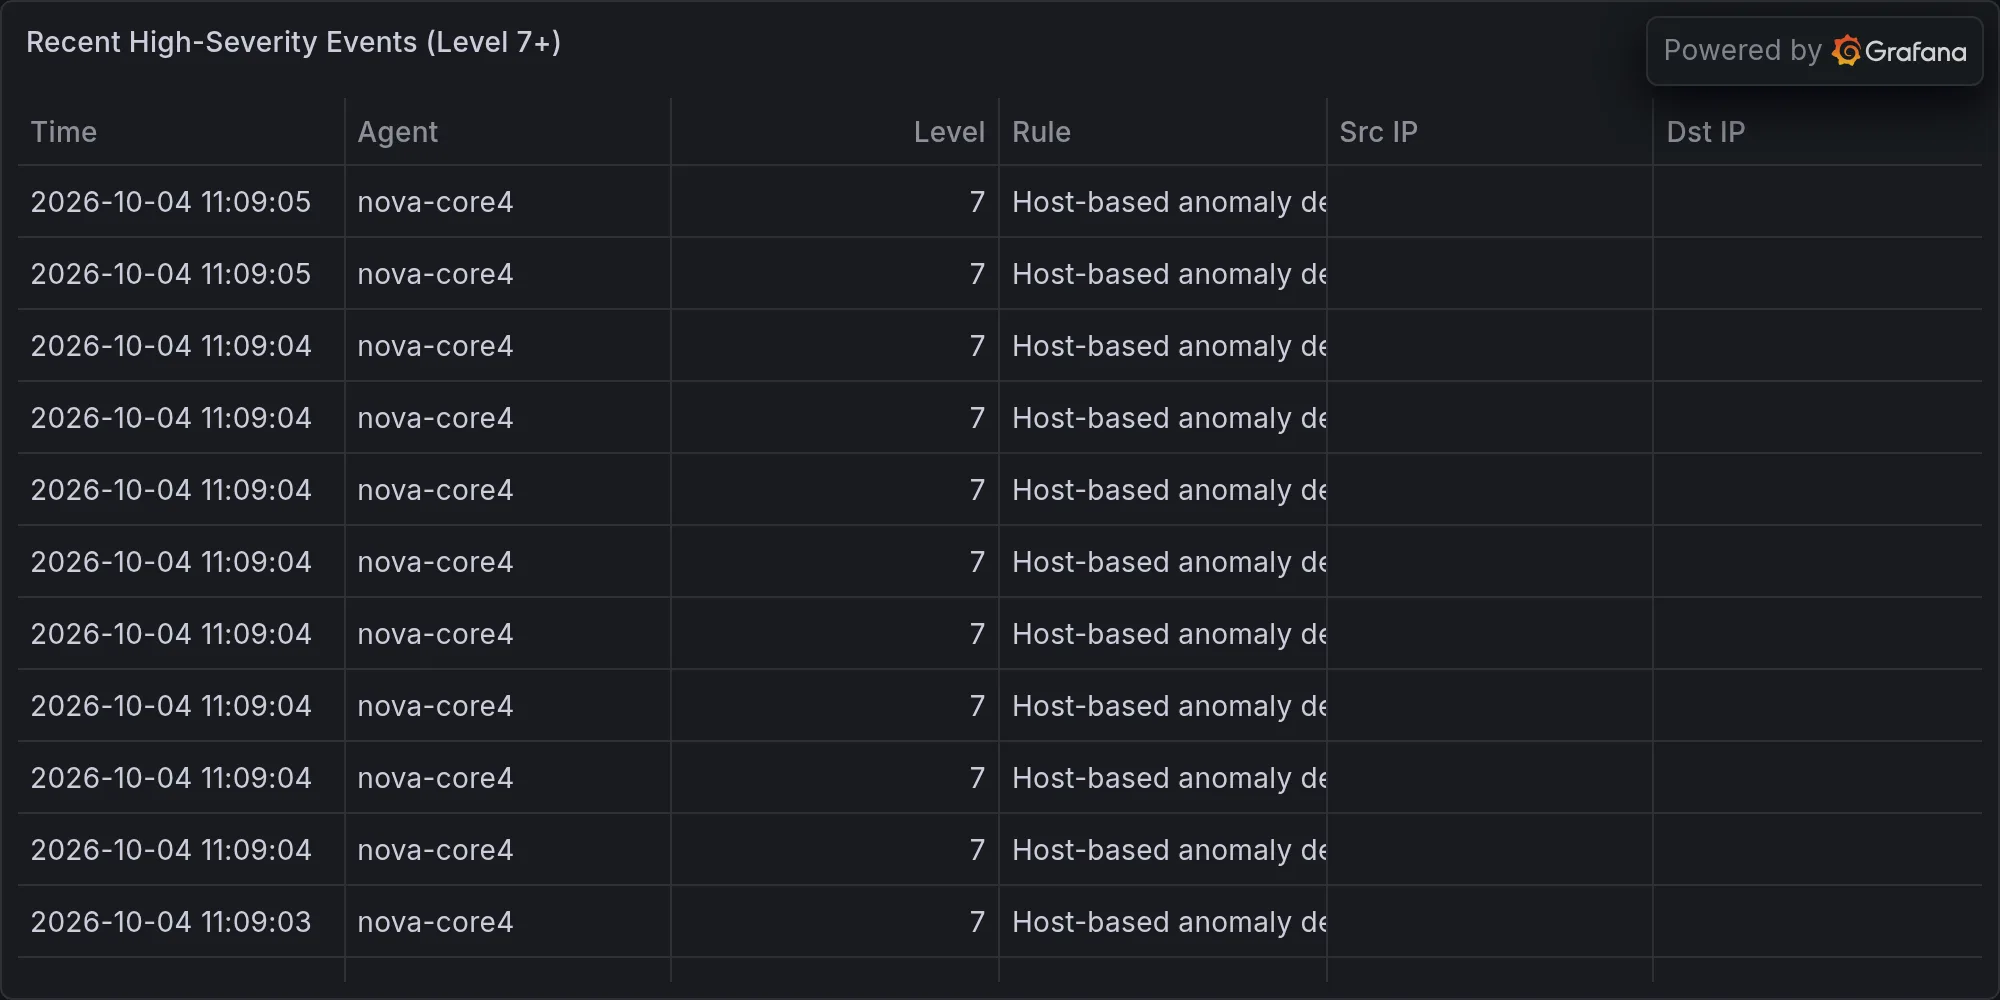
Recent high-severity events at publish time: