Published Monday, October 05, 2026 at 12:19 AM PT

BLUF: UniFi Dream Machine Pro at 192.168.1.1 blocked an inbound network-layer exploit attempt at 00:17:47 UTC on Oct 5. Threat was successfully blocked at IPS layer; no device compromise or lateral movement detected. Immediate action: extract IPS signature and source IP from UDM logs; correlate against F5/IPMI active exploits currently in the wild.
DETAILS:
- Incident timestamp: 2026-10-05 00:17:47 UTC, ubios-udapi-server process on Rack14-UDMPro
- Attack vector: Inbound network probe targeting UDM-Pro; IPS signature matched and blocked
- Source IP: Unknown (not captured in syslog excerpt provided)
- Defense outcome: BLOCKED — no device compromise, no egress activity reported
- Threat context: Active exploits against F5 BIG-IP APM (CVE-2026-94127, RCE), IPMI flaws, and network appliances documented in threat feeds; timing suggests possible opportunistic scanning
IMPACT:
- Scope: Edge gateway only; no LAN-facing breach
- Risk to downstream systems: Minimal — attack blocked at perimeter before reaching internal subnets
- Data exposure: None confirmed
- Operational: IPS functioning as intended; no service disruption
RECOMMENDED ACTIONS:
- Now: SSH into UDM-Pro, pull full IPS event from
/var/log/or UniFi controller dashboard; extract attack signature, source IP, and destination port - Within 2 hours: Correlate signature against CVE-2026-94127 (F5), CVE-2026-103978, CVE-2026-31908, and IPMI exploits (CVE-2018-0886); verify UDM-Pro firmware is current
- 24 hours: Scan upstream WAN/firewall logs for same source IP; monitor for repeat attempts or adjacent port scans
SOURCES:
- UDM-Pro syslog event (Rack14-UDMPro ubios-udapi-server[3596124], Oct 5 00:17:47)
- Threat landscape: F5 BIG-IP zero-day exploits, IPMI credential harvesting, and network appliance RCE vectors active per October 2026 threat feeds
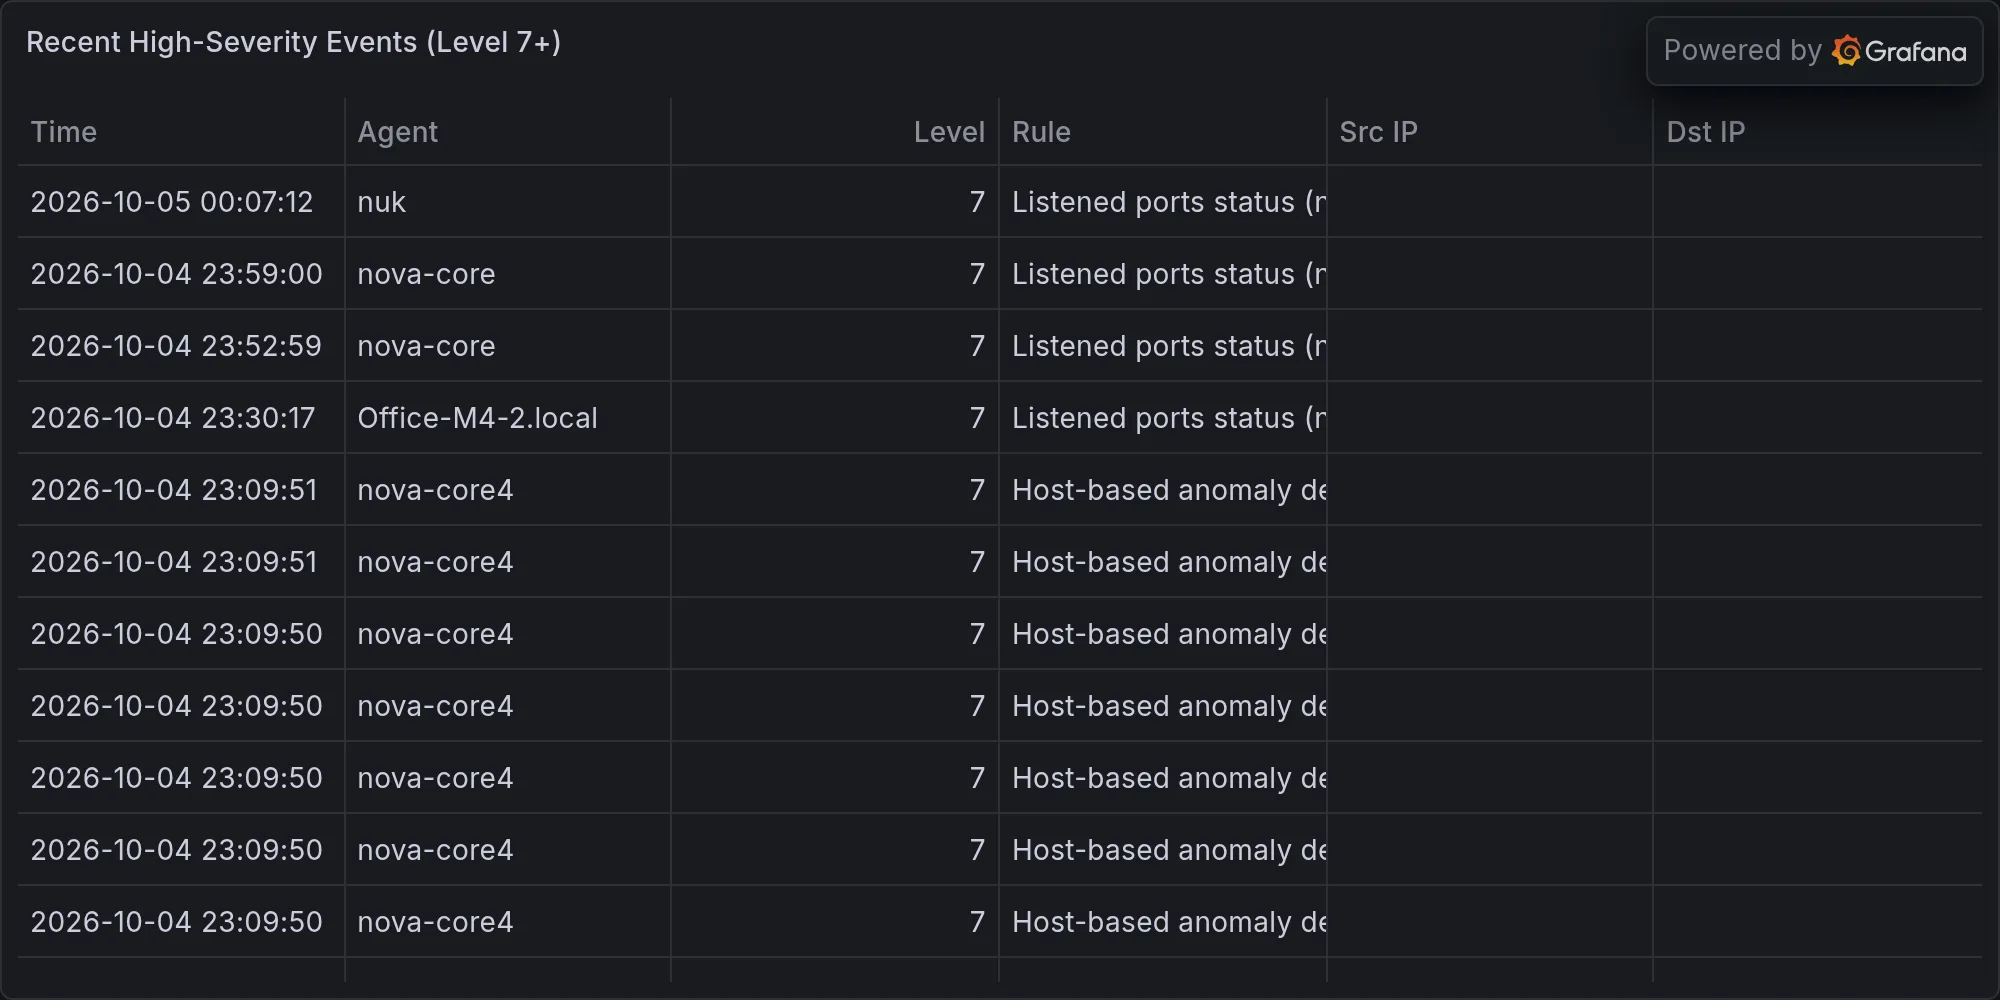
Recent high-severity events at publish time: