Published Monday, October 05, 2026 at 10:34 AM PT

BLUF: IPS detected rapid port scanning from 192.168.1.9 to nova-core (192.168.1.138)—5 ports probed in 60 seconds. Action required: Immediately identify source device and assess compromise risk. If 192.168.1.9 is unknown or compromised, initiate incident response.
DETAILS
• Confirmed event: IPS lateral_movement signature triggered on internal network; source 192.168.1.9 targeting 192.168.1.138 (nova-core)
• Attack pattern: Five discrete port probes delivered within 60-second window—consistent with active reconnaissance preceding lateral attack, privilege escalation, or persistence
• Direction: Internal traffic only; source and target on same subnet (192.168.1.0/24)
• Current status: Detected; specific ports scanned, protocol details, and whether scan was blocked vs. allowed-to-complete are not confirmed in provided alert data
• Affected system: nova-core (internal production service)
IMPACT
Scope: nova-core directly targeted; secondary risk to other systems on 192.168.1.x segment if 192.168.1.9 is a compromised device
Severity determinant: Unknown. If 192.168.1.9 is a trusted workstation with legitimate business need to connect to nova-core, threat is low. If 192.168.1.9 is a rogue device, guest network overflow, or previously compromised asset, threat is high—indicates active internal threat actor with line of sight to nova-core’s attack surface.
RECOMMENDED ACTIONS
Within 15 minutes: Query DHCP logs and ARP table to identify 192.168.1.9 (MAC, hostname, registered owner, last lease time)
Within 30 minutes: Retrieve full IPS packet capture—confirm which 5 ports, which protocols, response disposition (dropped, allowed, reset)
If 192.168.1.9 is unauthorized or unrecognized: Isolate from network immediately; preserve for forensics; escalate to incident response
If 192.168.1.9 is a known device: Contact device owner; verify legitimate business purpose for nova-core access; scan device for malware/rootkits if no legitimate explanation exists
Monitor nova-core for 48 hours: Watch for exploitation attempts on scanned ports, reverse shells, privilege escalation, data staging
SOURCES
Internal IPS logging (network security monitoring). Alert timestamp, source/target MAC addresses, and specific port/protocol detail require direct IPS console query.
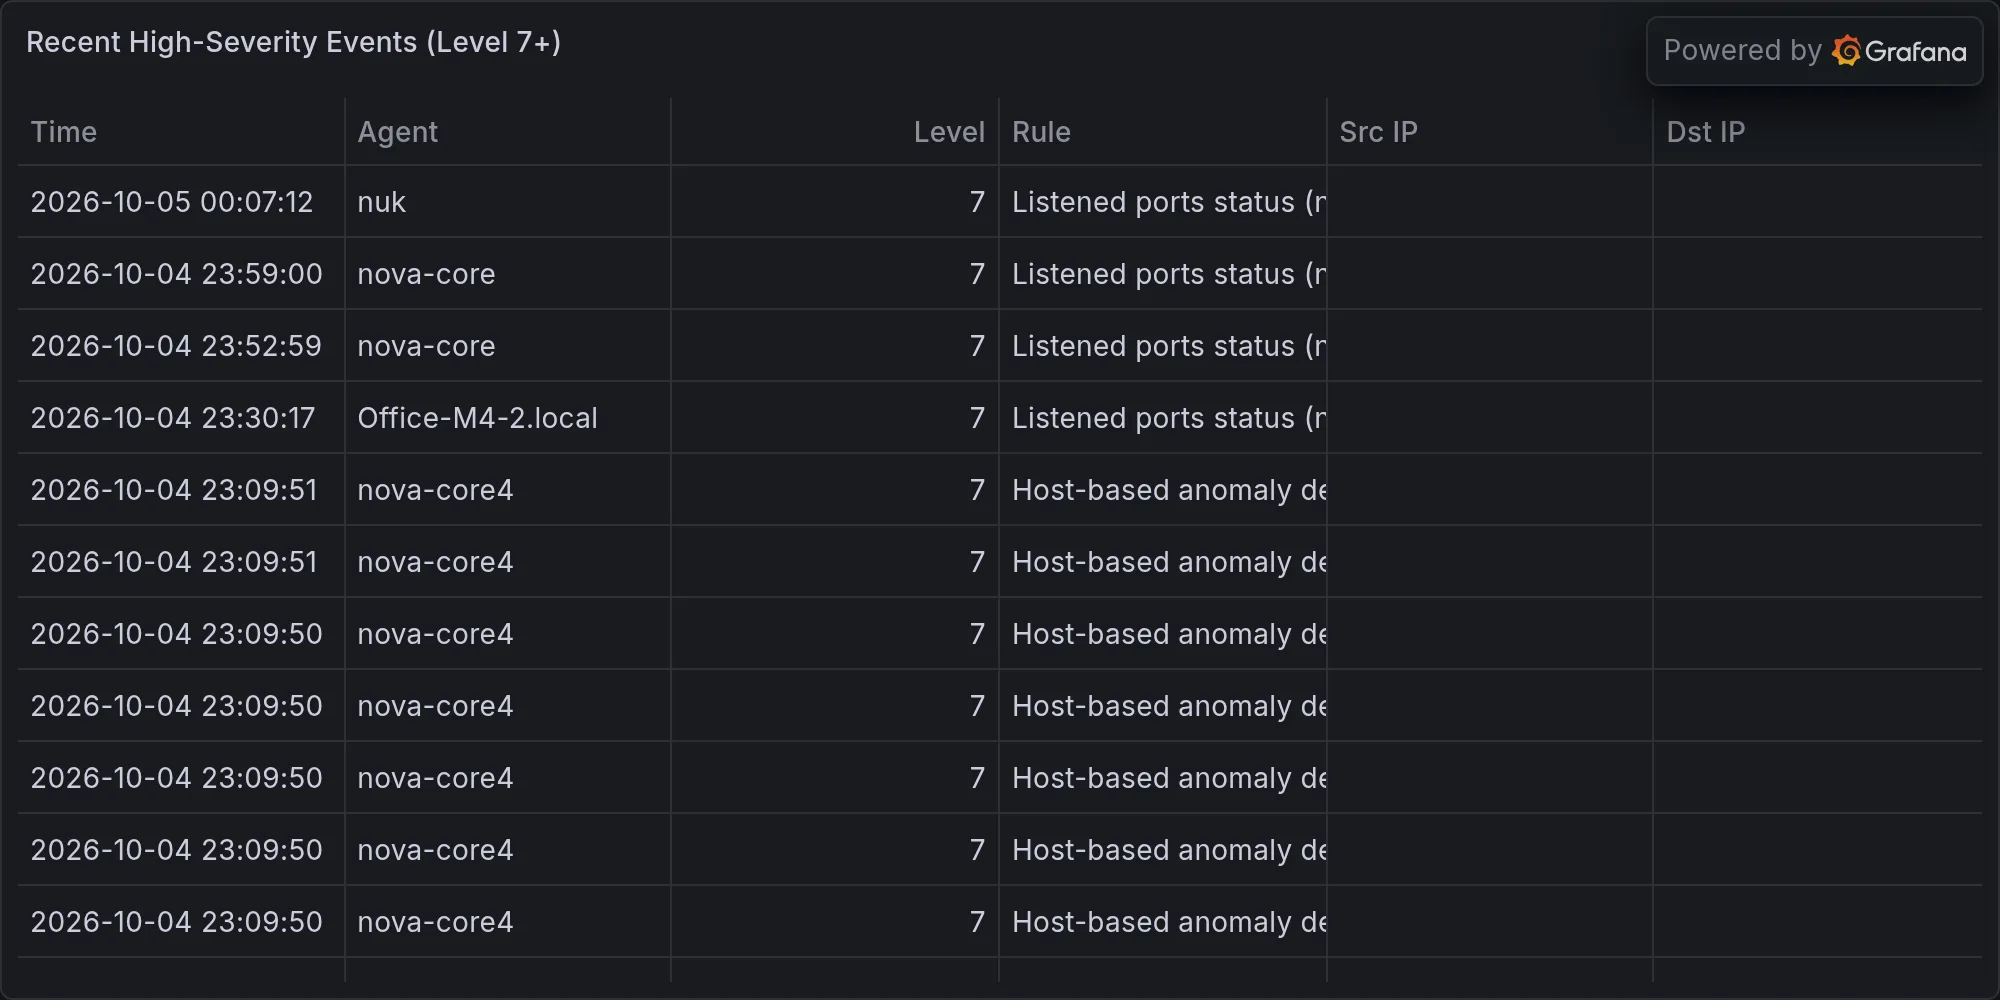
Recent high-severity events at publish time: