Published Tuesday, October 06, 2026 at 05:54 AM PT

An inbound intrusion attempt targeting your UniFi Dream Machine Pro (192.168.1.1) was blocked by IPS rules on 06 Oct 05:53:12 UTC. Attack source remains unknown. Ubiquiti disclosed critical RCE vulnerabilities in recent days; active exploitation campaigns are confirmed in the wild. Verify your UDM-Pro firmware is patched to latest release immediately. Monitor gateway logs for additional probe attempts.
DETAILS
- Event: IPS signature triggered on 192.168.1.1 (your UniFi gateway), inbound direction. Ubiquiti IPS rule set (CEF:0|Ubiquiti|UniFi Network|10.6) categorized threat as malicious; attack was blocked before reaching target.
- Source ambiguity: No source IP logged in trigger data. Likely spoofed, proxied, or source extraction failed in this log format—cannot attribute to known threat actor without full packet capture.
- Timing: Attack occurred during known active exploitation window for Ubiquiti zero-days (verified within last 24–48 hours across multiple security feeds tracking this cluster).
- Vulnerability context: Ubiquiti released urgent patches for three critical RCE flaws. Patch status of this UDM-Pro unknown; if running pre-patch firmware, this device is vulnerable. F5 BIG-IP APM zero-day (CVE-2026-94127) is also being weaponized in parallel campaigns, but this alert targets Ubiquiti asset.
- Broader threat cluster: Nova’s threat intel logs reference coordinated multi-vector attacks combining Chrome 0-day, UniFi exploits, macOS stealers, and VPN flaws—suggests organized campaign, not opportunistic scanning.
IMPACT
- Direct: Attack was blocked; no confirmed compromise of UDM-Pro at this time.
- Scope: Risk extends to all internal network traffic routed through this gateway; if UDM-Pro is compromised, attacker gains MITM position on LAN.
- Unconfirmed: Whether this probe is reconnaissance for a follow-up attack or part of automated scanning cannot be determined without fuller logs.
RECOMMENDED ACTIONS
- Immediate (next 1 hour): SSH to UDM-Pro, verify firmware version, confirm all patches from Ubiquiti’s latest release are applied. If behind, patch now.
- Next 24 hours: Pull full IPS/gateway logs from Rack14-UDMPro. Search for repeated probes from same or different sources; escalate if pattern indicates targeting behavior.
- Ongoing: Enable verbose IPS logging temporarily; flag any additional Ubiquiti-targeted signatures. Correlate with Nova’s threat-cluster tracking to assess if this site is being actively hunted.
SOURCES
- Ubiquiti UniFi IPS alert (CEF format, 06 Oct 05:53:12)
- Nova threat intelligence (multi-vector cluster, F5 BIG-IP CVE-2026-94127 exploitation, Ubiquiti patch releases)
- News4Hackers, Hacker News, SecurityAffairs, SOC Prime (Ubiquiti RCE disclosures, confirmed active exploitation)
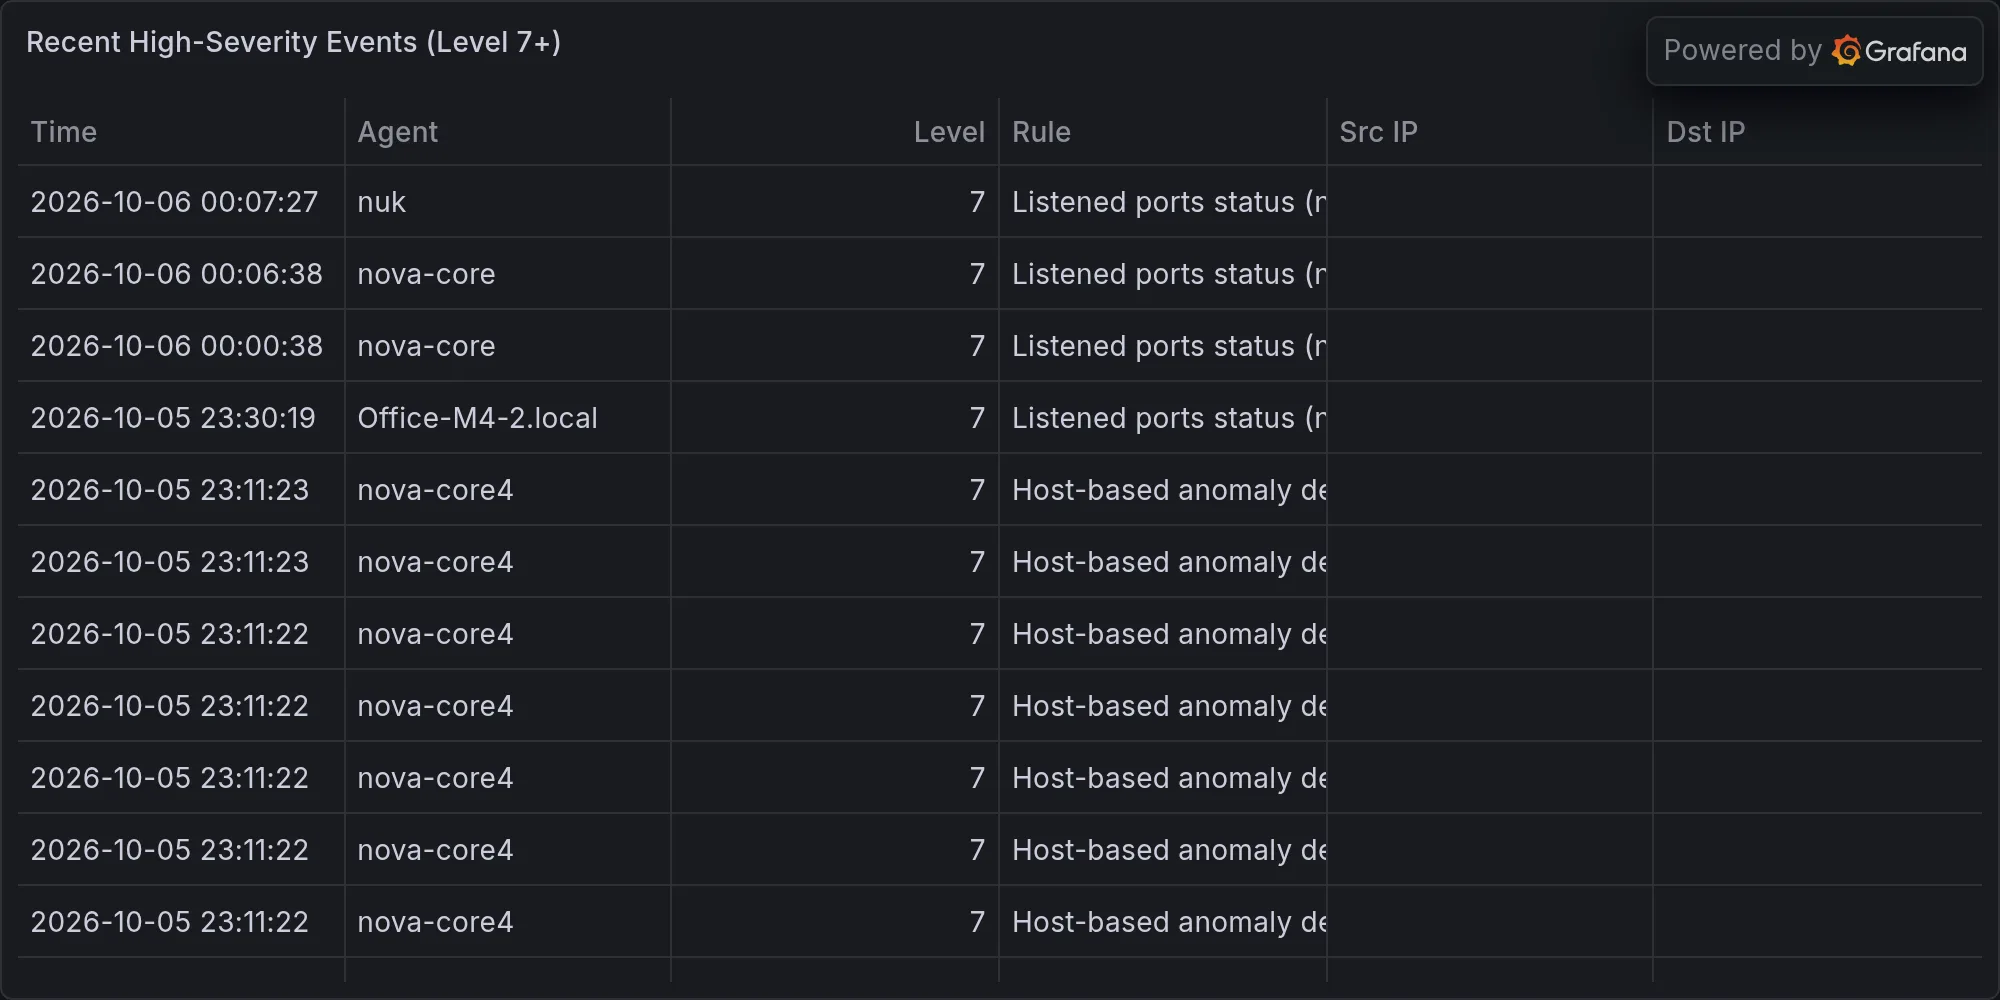
Recent high-severity events at publish time: