Published Tuesday, October 06, 2026 at 12:19 AM PT

BLUF: Ubiquiti UDM-Pro gateway (192.168.1.1) detected and blocked an inbound exploit attempt targeting ubios-udapi-server at 00:17:46 UTC on Oct 6. Attack source unknown. No payload reached the device; network posture intact.
DETAILS:
- Event: Intrusion Prevention System (IPS) signature match, inbound direction, blocked before execution
- Device: Rack14-UDMPro (192.168.1.1) — internal network gateway; ubios-udapi-server service (PID 3067133)
- Timestamp: October 6, 2026, 00:17:46 UTC
- Attack Source: Unknown — IP address and geolocation not provided in initial IPS event
- Disposition: Blocked by IPS rule; no outbound callback, no payload execution, no device compromise
IMPACT:
- Scope: Network perimeter only; no internal systems directly exposed
- Risk Status: Contained
- Business Impact: None detected; network services operational
RECOMMENDED ACTIONS:
- Now: Export UDM-Pro IPS event logs (attack signature, source IP, destination port/service); check for additional attempts in ±2 hours around 00:17:46
- Within 2 hours: Verify UDM-Pro firmware is current version; confirm ubios-udapi-server is not running known vulnerable software versions
- Within 4 hours: Correlate IPS signature against active CVE feed (note: CVE-2026-94127, CVE-2026-103978, CVE-2026-31908, CVE-2026-102971, CVE-2026-102973 noted in threat intelligence but CVE match is unconfirmed from log alone)
- Within 24 hours: Review firewall ingress rules; if source IP geolocated, consider regional block; monitor for pattern escalation
SOURCES:
- Ubiquiti UDM-Pro ubios-udapi-server IPS log, Oct 6 00:17:46
- Nova security memory (CVE threat feed context; specific CVE attribution requires IPS signature analysis)
STATUS: Developing — signature identification in progress. Event contained; no further action required until log analysis complete.
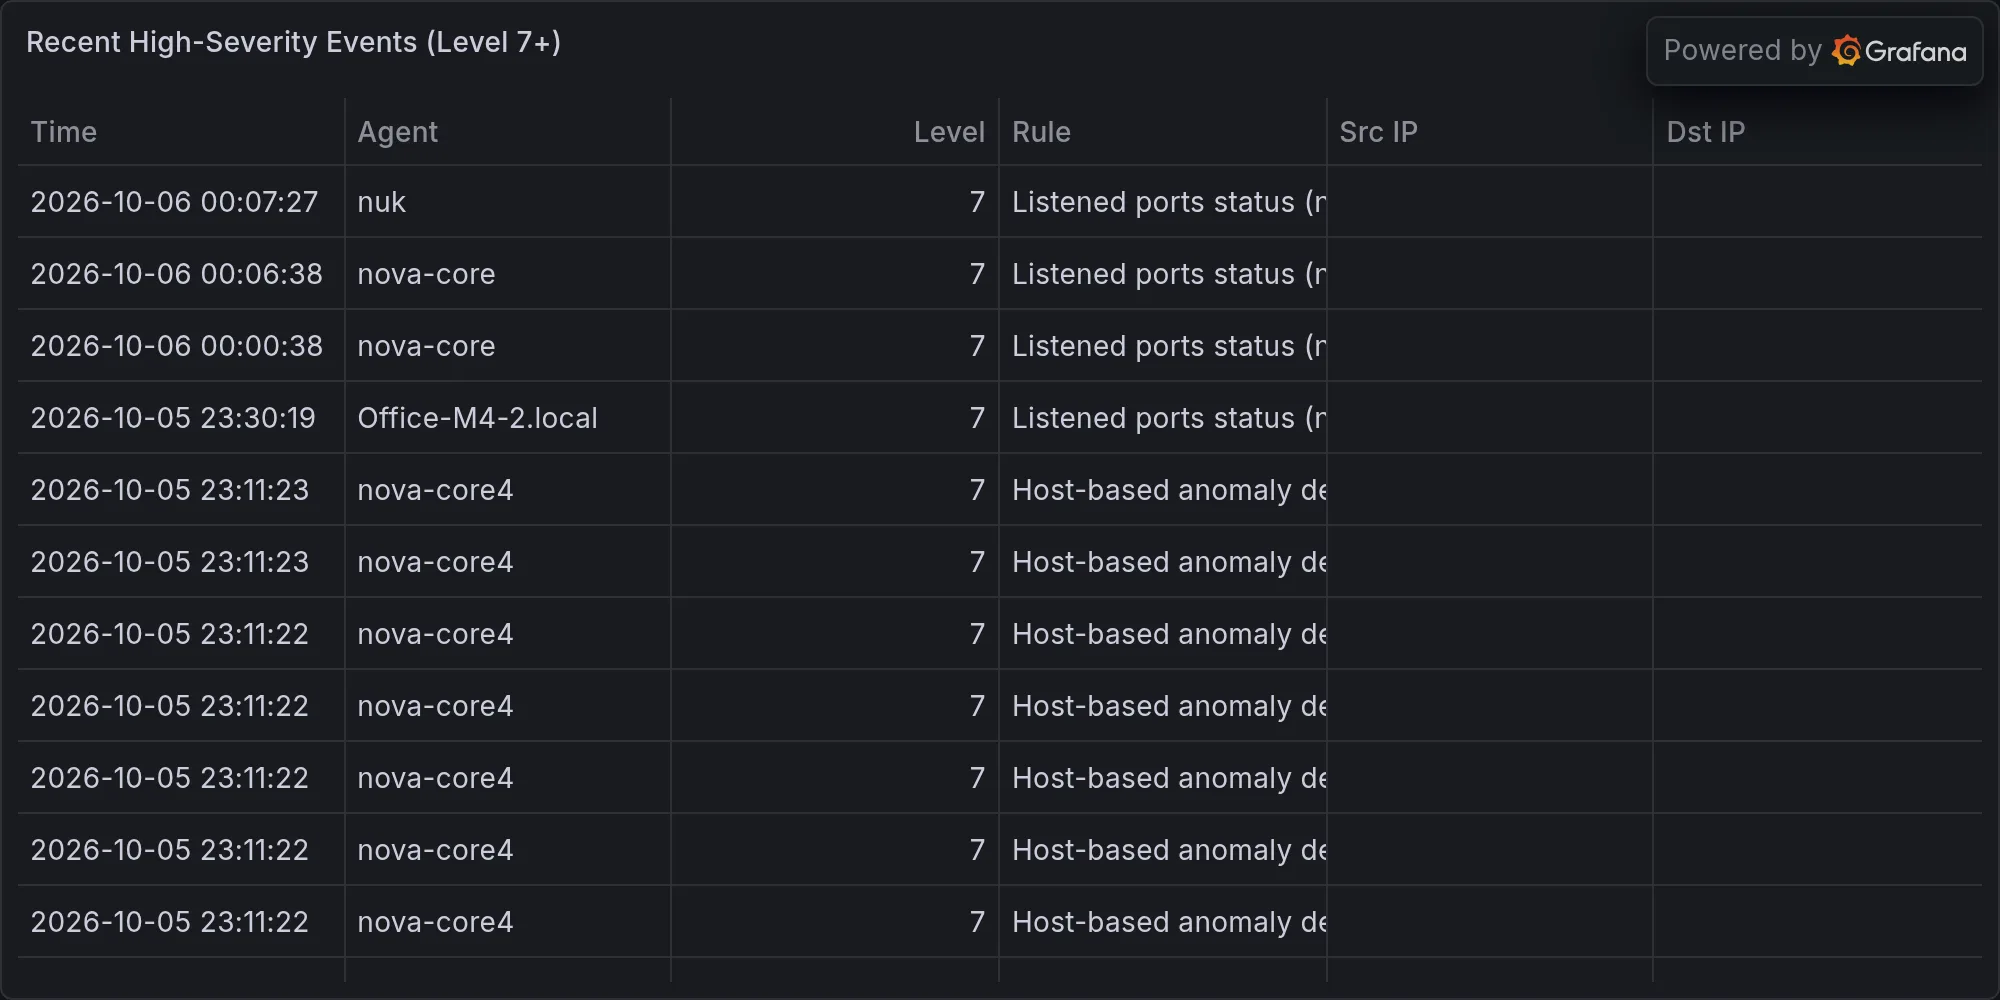
Recent high-severity events at publish time: