Published Tuesday, October 06, 2026 at 11:54 AM PT

BLUF: UniFi IPS blocked an inbound attack at 11:53:12 UTC on 2026-10-06 against the network gateway (192.168.1.1); attack source and payload type are unknown. Review IPS logs and full packet capture immediately — this overlaps an active exploit window for F5 BIG-IP APM (CVE-2026-94127), Ubiquiti critical patches, and Chrome 0-day.
DETAILS
- IPS Alert: Ubiquiti UniFi Network (Rack14-UDMPro, firmware 10.6) triggered attack_response at 11:53:12 UTC on 2026-10-06.
- Target: Gateway 192.168.1.1 (inbound direction).
- Action: Blocked—traffic did not reach interior network.
- Source IP: Unknown (not recorded in available alert summary).
- Attack Type: Unknown—IPS signature/classification not provided in trigger data.
- Threat context: Active zero-day exploits circulating for F5 BIG-IP APM, Ubiquiti infrastructure, Chrome, and VPN implementations. Multi-vector attack cluster reported by security agencies.
IMPACT
- Scope: Inbound perimeter only; interior network unaffected (IPS blocked before egress to LAN).
- Affected systems: UniFi gateway and monitoring tier aware of the attempt.
- Data exposure: None confirmed; successful block suggests no compromise.
- Operational impact: None detected. IPS functioning as designed.
RECOMMENDED ACTIONS
Immediate (next 30 min):
- Export full IPS logs from Rack14-UDMPro covering 11:50–12:00 UTC.
- Retrieve pcap/packet capture if available; identify source IP, destination ports, payload characteristics.
- Confirm IPS firmware version and signature database date—ensure latest definitions are loaded.
Within 2 hours:
- Cross-check source IP against known threat actor ranges (GreyNoise, AbuseIPDB).
- If source is a residential/datacenter IP, check for reverse DNS or historical abuse reports.
- Query gateway logs for any anomalous traffic patterns before/after 11:53:12 UTC.
Ongoing:
- Patch UniFi controller and UDM Pro to latest available versions (critical Ubiquiti patches pending).
- Monitor F5 BIG-IP systems if any exist on the network; apply CVE-2026-94127 patch immediately.
- Review egress filtering rules for C2 beacons or data exfil attempts (if IPS severity suggests reconnaissance).
SOURCES
- UniFi IPS event log, 2026-10-06 11:53:12 UTC (IPS device: Rack14-UDMPro).
- Active threat cluster: F5 BIG-IP APM CVE-2026-94127 (unauthenticated RCE), Ubiquiti critical vulnerabilities, Chrome 0-day, macOS stealer variants, VPN exploits (SecurityWeek, SOC Prime, TheHackerNews, TheRegister).
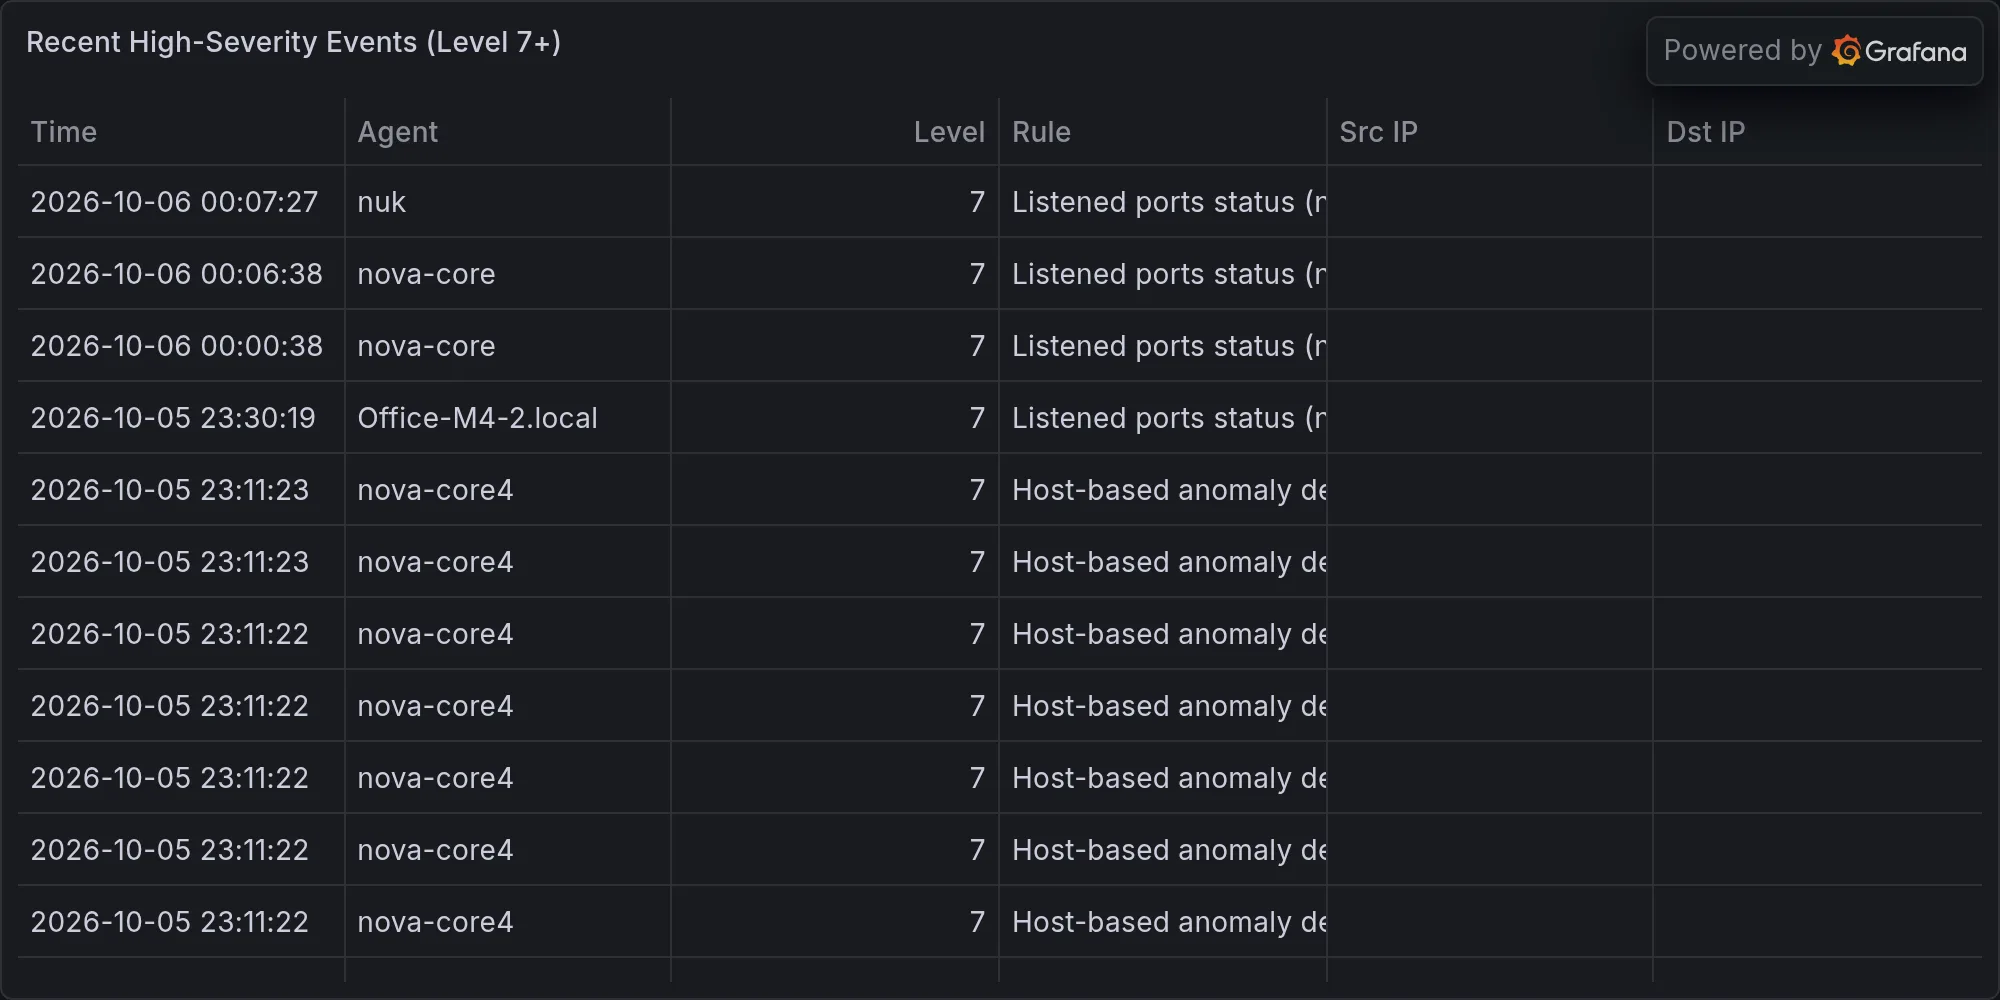
Recent high-severity events at publish time: