Published Wednesday, October 07, 2026 at 12:19 AM PT

BLUF: UDM-Pro firewall (192.168.1.1) blocked an inbound exploit attempt at 00:18:09 UTC on Oct 7. Source IP unknown. No breach confirmed; payload stopped before delivery. Verify device integrity and review IPS logs for attack signature matching.
DETAILS:
- Device affected: Ubiquiti Dream Machine Pro (UDM-Pro), 192.168.1.1, Rack14
- Detection time: 2026-10-07 00:18:09 UTC
- IPS action: Blocked (threat did not penetrate)
- Attack source: Unknown/not logged in available context
- Vulnerability target: ubios-udapi-server process (details insufficient to confirm specific CVE)
IMPACT:
- Scope: Single edge device; no indication of lateral movement or secondary compromise
- Risk: Contained if IPS signature matched the actual exploit; signature mismatch would mean threat remains present
- Affected systems: UDM-Pro management interface and API surface
RECOMMENDED ACTIONS:
- Pull full UDM-Pro IPS logs (signature name, rule ID, payload details) from Rack14-UDMPro to identify the exact CVE
- Audit UDM-Pro system logs for failed API calls or unusual activity in the same ~2min window
- Check device firmware version against known ubios-udapi-server vulnerabilities (cross-reference with Ubiquiti security advisories)
- If device runs older firmware: schedule immediate patch; if current, escalate to Ubiquiti support with the IPS event details
SOURCES: Ubiquiti Networks UDM-Pro IPS log (2026-10-07 00:18:09). Attack signature identity unconfirmed — IPS rule data required to map to CVE.
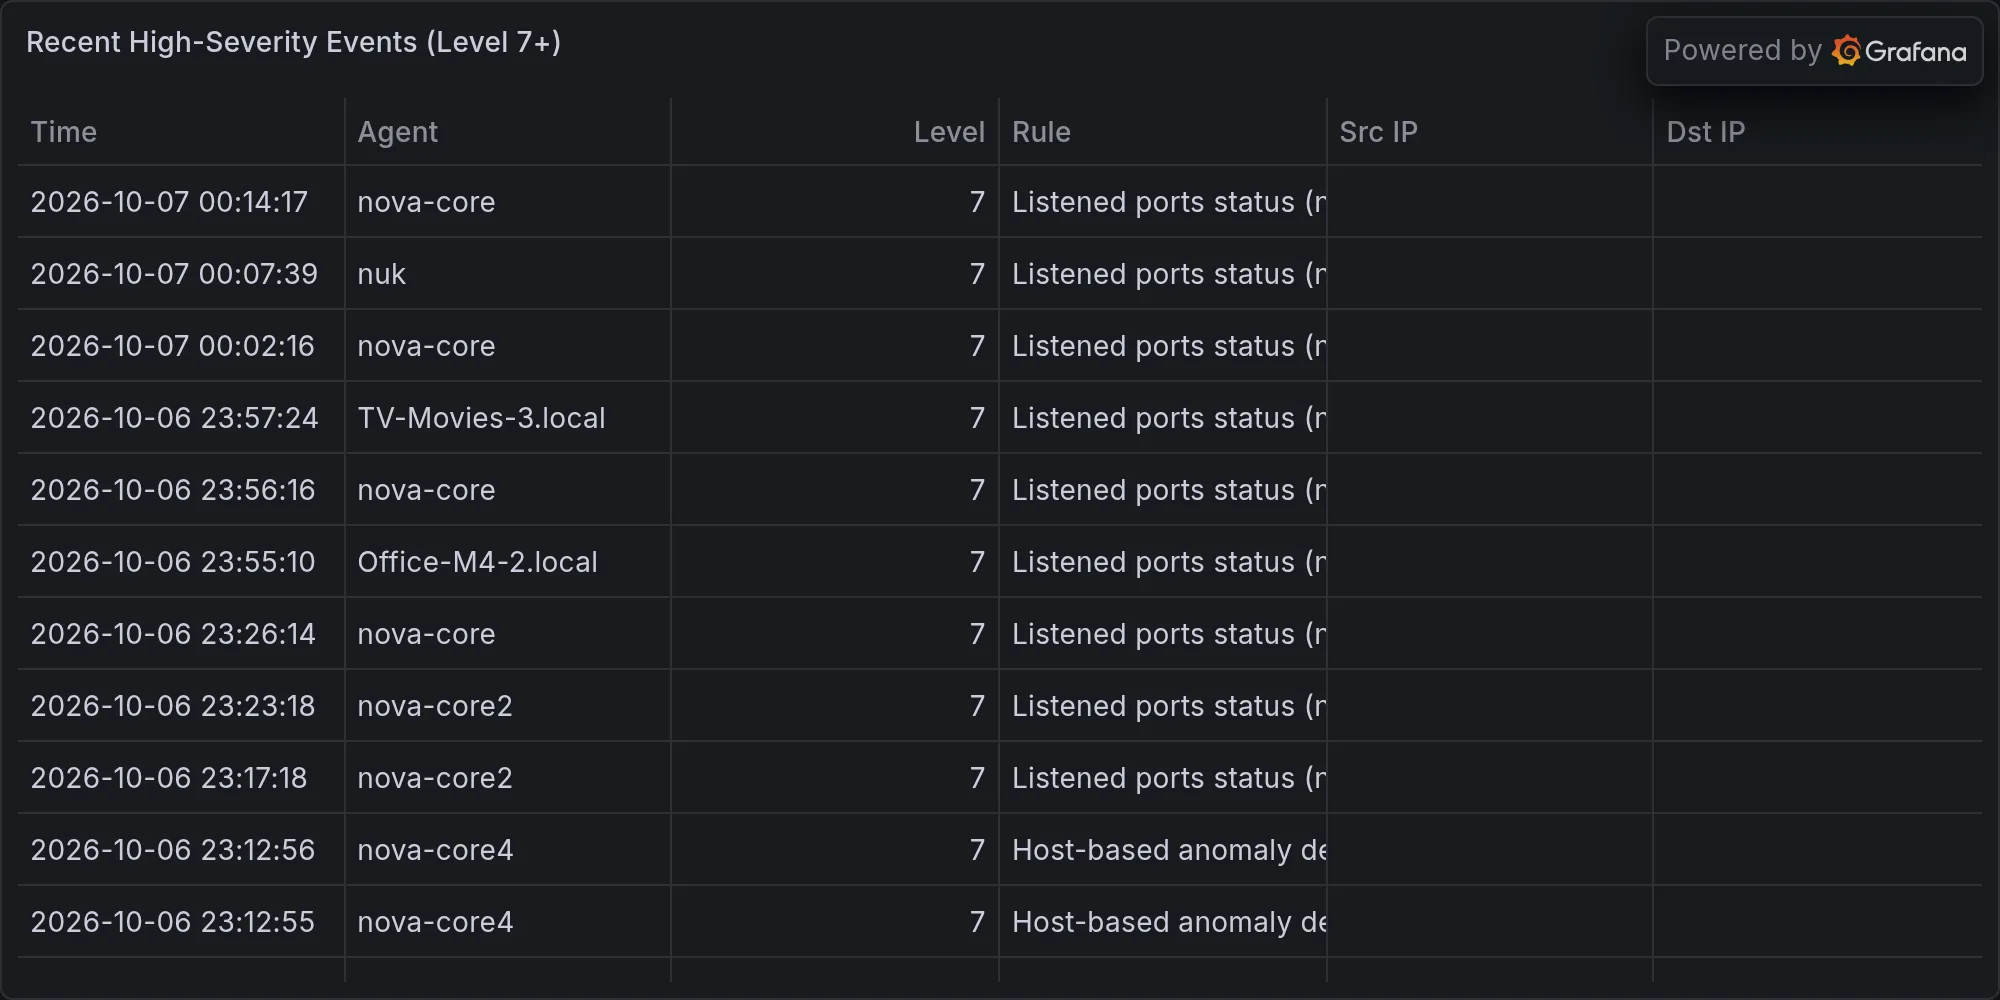
Recent high-severity events at publish time: