Published Wednesday, October 07, 2026 at 05:59 AM PT

BLUF: UniFi Dream Machine Pro at 192.168.1.1 triggered an IPS block on inbound malicious traffic at 05:57 UTC Oct 7, 2026. Source unknown; attack was blocked before reaching internal network. Event correlates with active zero-day exploitation campaign targeting F5 BIG-IP APM (CVE-2026-94127) and multiple Ubiquiti vulnerabilities documented in recent security disclosures. No compromise confirmed; immediate network audit recommended.
DETAILS
- Event: Ubiquiti UniFi Network v10.6 IPS alert (CEF) logged on Rack14-UDMPro (192.168.1.1) at 05:57:24 UTC today; inbound traffic detected and blocked at network perimeter.
- Attack details: Source IP unknown; payload unconfirmed; action taken was blocked — traffic did not reach internal systems.
- Threat context: Active exploitation confirmed in wild for F5 BIG-IP APM zero-day (CVE-2026-94127) enabling unauthenticated RCE; Ubiquiti has issued urgent patches for multiple critical vulnerabilities in recent days.
- Broader cluster: Multiple security vendors reporting coordinated multi-vector attacks combining Chrome 0-day exploits, UniFi/network device attacks, macOS stealers, and VPN bypass techniques — suggests organized threat actor activity, not opportunistic scanning.
IMPACT
- Scope: Home network perimeter only; no internal systems compromised (attack was blocked at gateway).
- Exposure: If UniFi gateway or related network devices are running outdated firmware or unpatched versions of known Ubiquiti vulnerabilities, repeat or follow-up attacks are likely.
- Risk level: Medium-High. Firewall performed its job, but the presence of sophisticated inbound traffic suggests persistent reconnaissance or direct targeting. Source anonymity prevents attribution.
RECOMMENDED ACTIONS
- Immediate: Verify Ubiquiti firmware version on gateway and all managed switches/APs is current; apply latest security patches if available.
- 24 hours: Review IPS logs for attack signatures/patterns; determine if F5 APM or other known zero-day exploitation techniques were present.
- Network audit: Check for any anomalous internal traffic or lateral movement; confirm no low-trust VLANs were accessed.
- Threat intelligence: Cross-reference source IP (if captured in full logs) against known malicious ASNs tied to CVE-2026-94127 campaigns.
SOURCES
- Ubiquiti UniFi Network IPS event log (Oct 7, 05:57 UTC)
- News4Hackers, SecurityWeek, TheRegister, SecurityAffairs: F5 BIG-IP APM CVE-2026-94127 active exploitation reporting
- SOC Prime, News4Hackers: Ubiquiti critical vulnerability warnings (dates recent)
- Multi-source: Cross-vector threat cluster documentation (Chrome, UniFi, macOS, VPN components)
STATUS: Developing — blocked threat; monitoring for repeat attempts and downstream indicators.
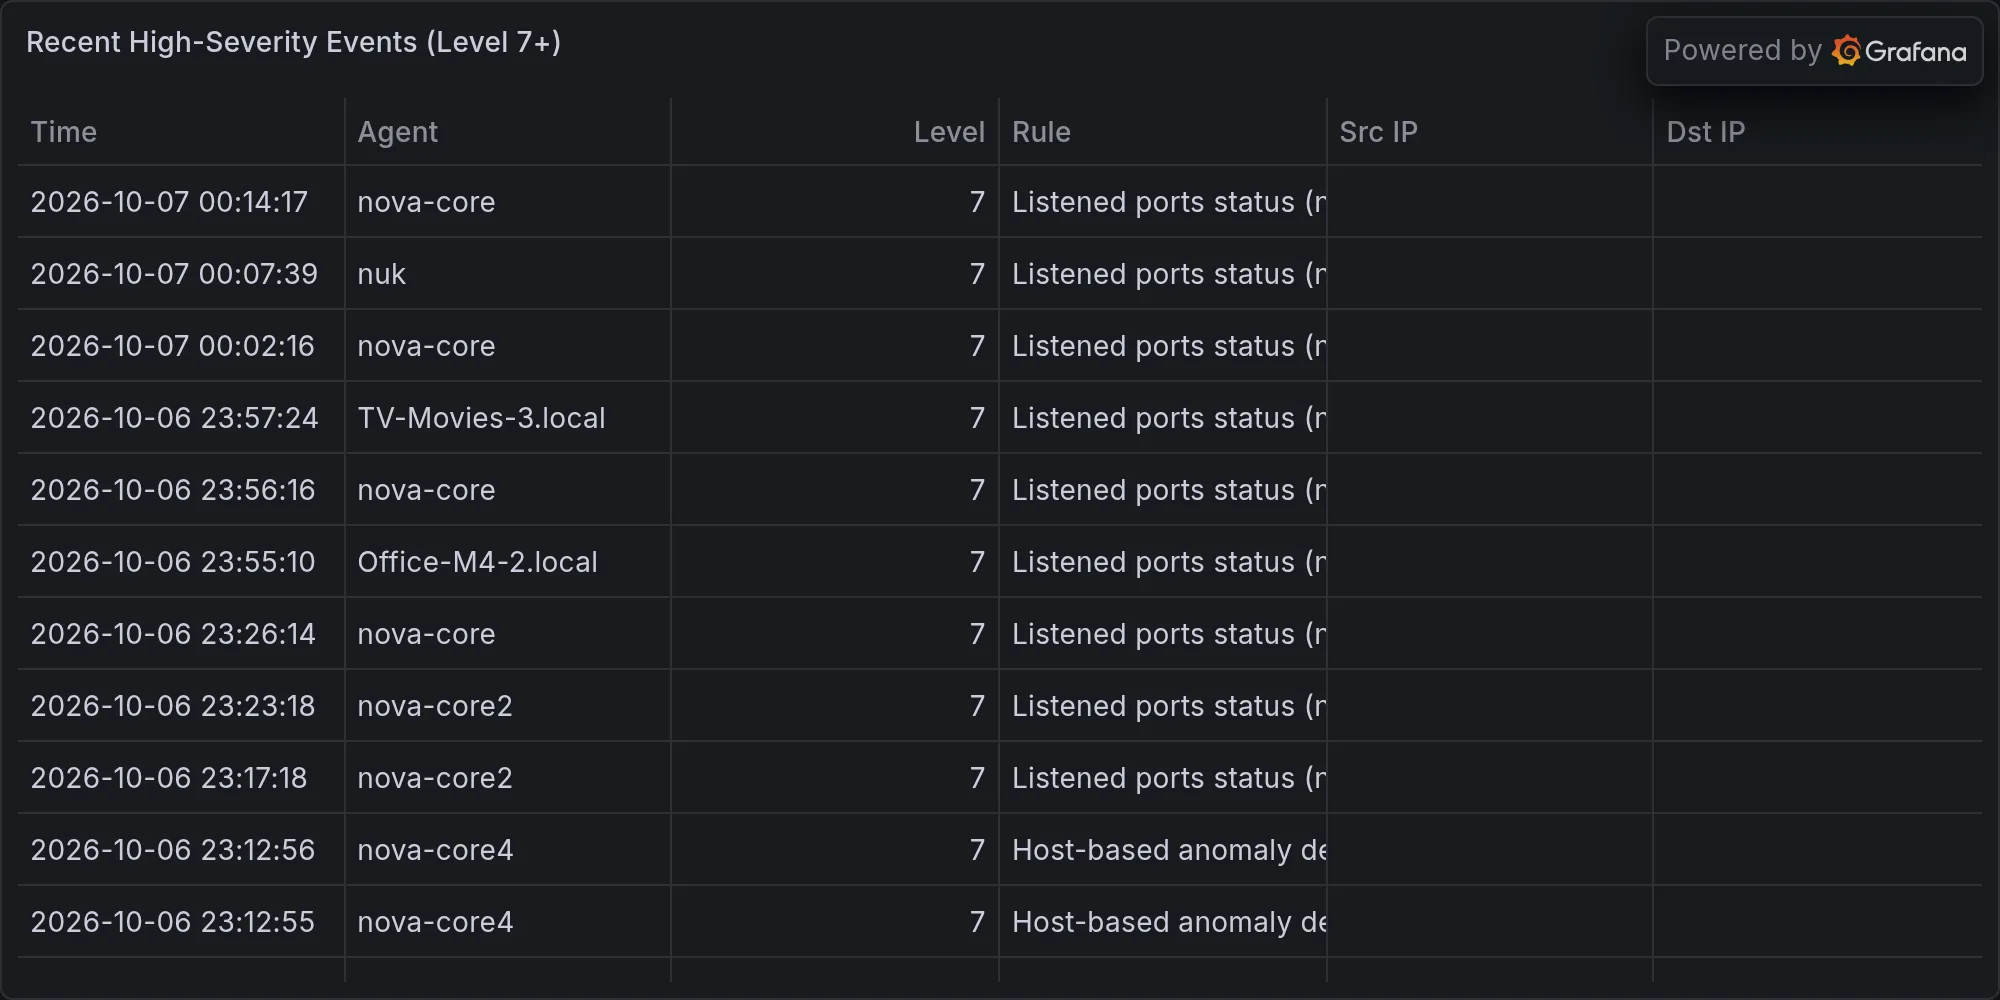
Recent high-severity events at publish time: