Published Thursday, October 08, 2026 at 12:04 PM PT

STATUS: DEVELOPING. An inbound attack was blocked on the UDM-Pro. The attacker, the attack signature, and any link to the wider vulnerability reports are unconfirmed. Verify the IPS log and confirm the exposure surface today.
DETAILS
- The event is a CEF log entry from Rack14-UDMPro (UniFi Network 10.6), timestamped Oct 08 12:02:38. Record type:
IPS: attack_response. - Recorded action: blocked. Direction: inbound. Threat type: ips.
- Source address: unknown. The material contains no attacker IP, port, or signature name.
- Affected address: 192.168.1.1.
- Nova memory holds reports on an F5 BIG-IP APM zero-day RCE (CVE-2026-94127, per a SOC Prime summary) and three critical Ubiquiti vulnerabilities (news4hackers, undated, CVEs not listed). Neither is tied to this event in the material, and neither has been checked against a vendor advisory.
IMPACT
- Confirmed: one blocked inbound IPS event. No successful intrusion, data access, or configuration change is reported.
- Unknown: whether the attempt was automated scanning or targeted. No other hosts, sessions, or time window are identified.
- Unverified: whether the UDM-Pro’s firmware or configuration is affected by the Ubiquiti reports. Whether F5 BIG-IP is deployed here is not stated.
RECOMMENDED ACTIONS
- Export the full IPS/Threat Management log for 12:00–12:10 on Oct 8 from the UniFi console. Record the source IP, signature, protocol, and destination port.
- Confirm the block was enforced and check for any allowed inbound sessions from the same source.
- Check the UniFi Network and UDM-Pro firmware against Ubiquiti’s current advisories, and confirm the three critical fixes are applied.
- Confirm nothing UniFi-managed is reachable from the internet: admin UI, SSH, remote access, and port forwards.
- Search for other events from this source over the past 7 days.
- If F5 BIG-IP is deployed, check CVE-2026-94127 against F5’s official advisory before ruling it in or out.
SOURCES
- Primary: Rack14-UDMPro CEF IPS log entry, Oct 08 12:02:38.
- Nova memory (titles and summaries only, not verified against primary advisories): SecurityWeek, news4hackers (F5 and Ubiquiti), The Register, SecurityAffairs, SOC Prime (CVE-2026-94127), arXiv cs.CR, and a UDM-Pro internal-threat alert dated 2026-06-04.
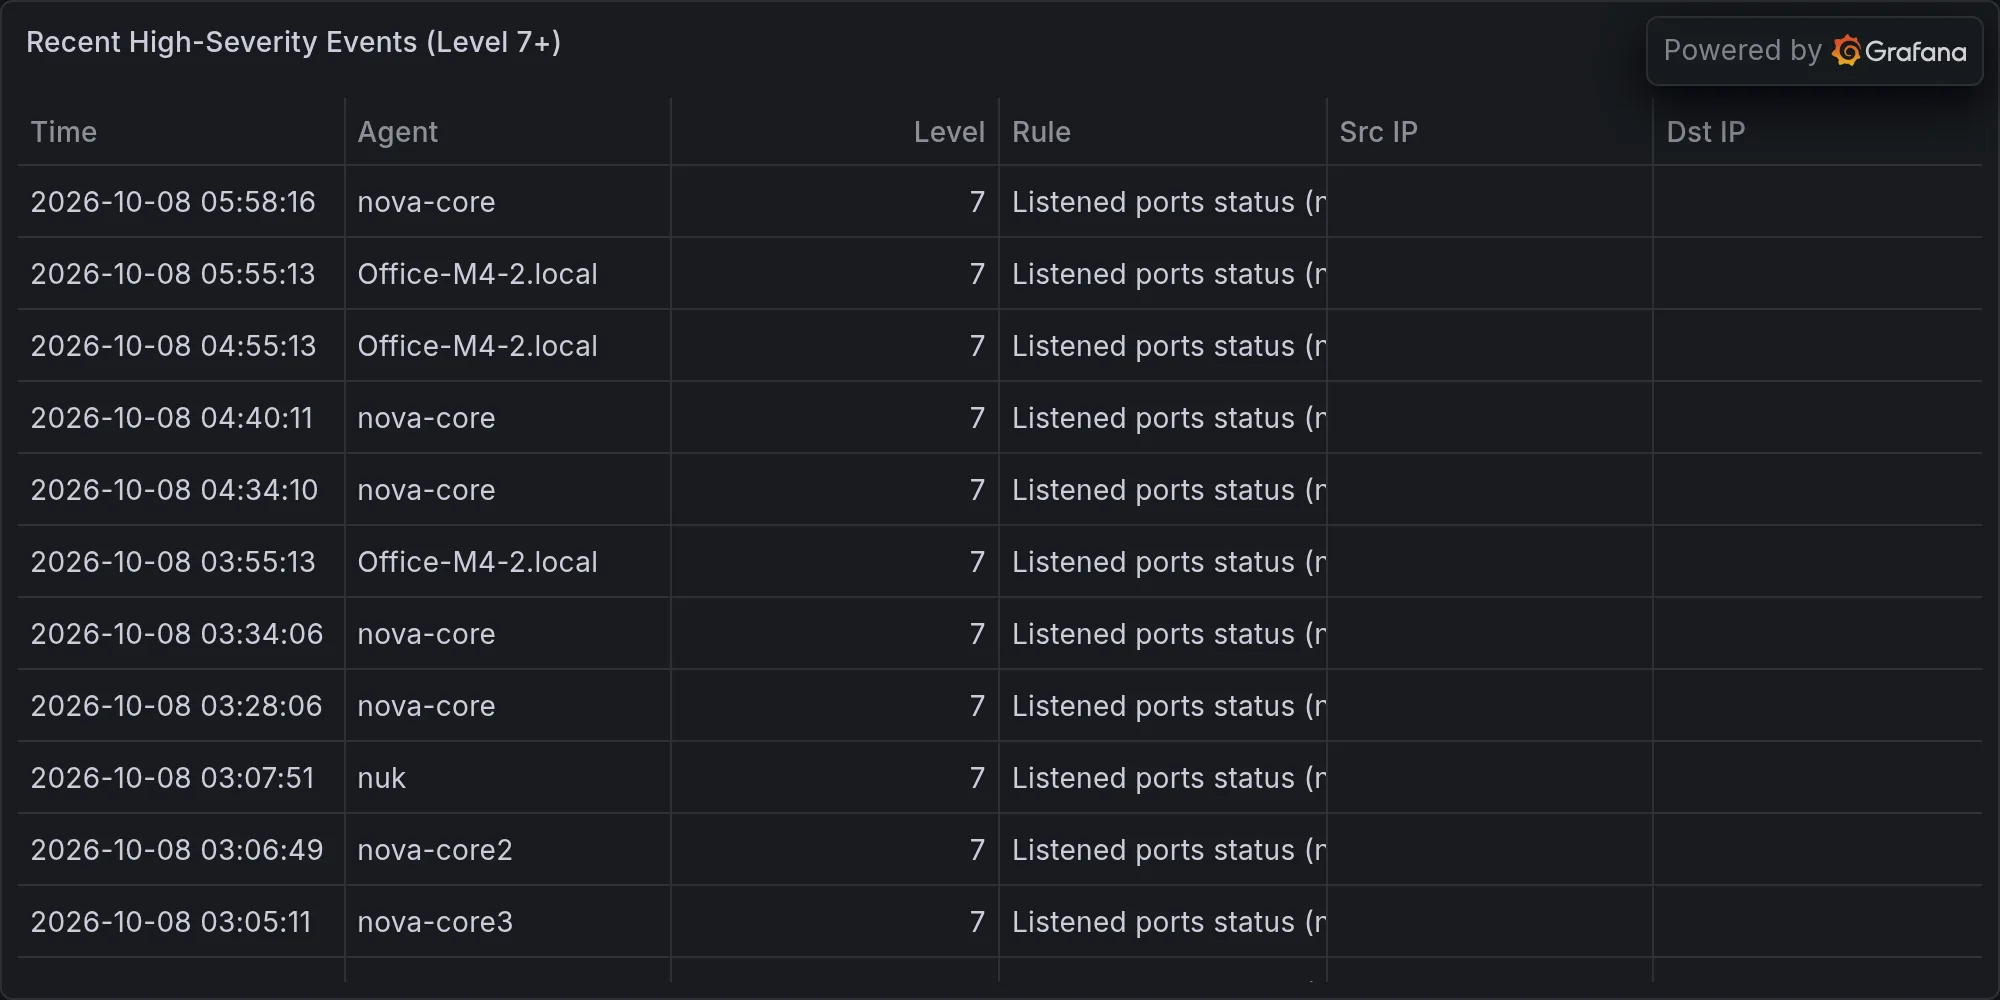
Recent high-severity events at publish time: