Published Thursday, October 08, 2026 at 12:19 AM PT

DEVELOPING: Event confirmed by one IPS log line. Attack details are unverified.
An inbound attempt classified as “exploit” targeted 192.168.1.1 (Rack14-UDMPro) and was blocked by the UDM-Pro intrusion prevention system (IPS) at Oct 8 00:18:14 log time. The attacker’s source and the vulnerability targeted are unidentified. No compromise is confirmed.
DETAILS
- The UDM-Pro IPS logged an event of type “exploit” against 192.168.1.1 at Oct 8 00:18:14 (log source: ubios-udapi-server, host Rack14-UDMPro).
- Logged action: blocked. Direction: inbound. Source: unknown.
- The log does not name a CVE, signature ID, protocol, or port, so the targeted vulnerability is unconfirmed.
- The material contains no evidence of follow-on activity, such as an allowed connection, lateral movement, or configuration change.
- Nova’s memory holds recent reports of other exploited vulnerabilities, including a critical F5 BIG-IP APM zero-day (CVE-2026-94127). Nothing in this event links to them. Treat that as unrelated until the IPS signature is checked.
IMPACT
- Affected: the device at 192.168.1.1 (Rack14-UDMPro). Other hosts behind it are not known to be affected.
- Confirmed impact: none beyond the blocked attempt.
- Unresolved: whether this was a targeted attack or automated scanning. A prior Nova memory entry labels a UDM-Pro IPS event as an “internal threat.” This event is logged as inbound with an unknown source, so its origin classification is unresolved.
RECOMMENDED ACTIONS
- Pull the full IPS record for the Oct 8 00:18:14 event: signature ID, CVE mapping, protocol, port, and source IP.
- Confirm that UniFi OS and the IPS signature database on Rack14-UDMPro are up to date.
- Review logs for the same source, or similar events, for 24 hours before and after. Check for any allowed traffic from that source.
- If the source is internal, investigate that host. If it is external and recurring, consider a blocklist rule.
- Escalate to a full incident only if step 3 shows allowed traffic or unexpected changes.
SOURCES
- UDM-Pro IPS log entry, Rack14-UDMPro, Oct 8 00:18:14 (provided event trigger).
- Nova memory: SOC Prime, “CVE-2026-94127: Critical F5 BIG-IP APM Zero-Day Exploited for Remote Code Execution.”
- Nova memory: news4hackers, “F5 BIG-IP Zero-Day Vulnerability Exploited – Critical Security Alert” and “F5 BIG-IP APM Zero-Day Vulnerability Patched After RCE Exploit.”
- Nova memory: internal alert titled “SECURITY ALERT — INTERNAL THREAT BLOCKED | UDM-PRO IPS EVENT” (dated 2026-06-04 in its image path).
- Nova memory: sploitus entries for CVE-2024-29415, CVE-2013-4784, CVE-2018-0886, CVE-2026-31908, CVE-2026-102971, and CVE-2026-103978. None is linked to this event.
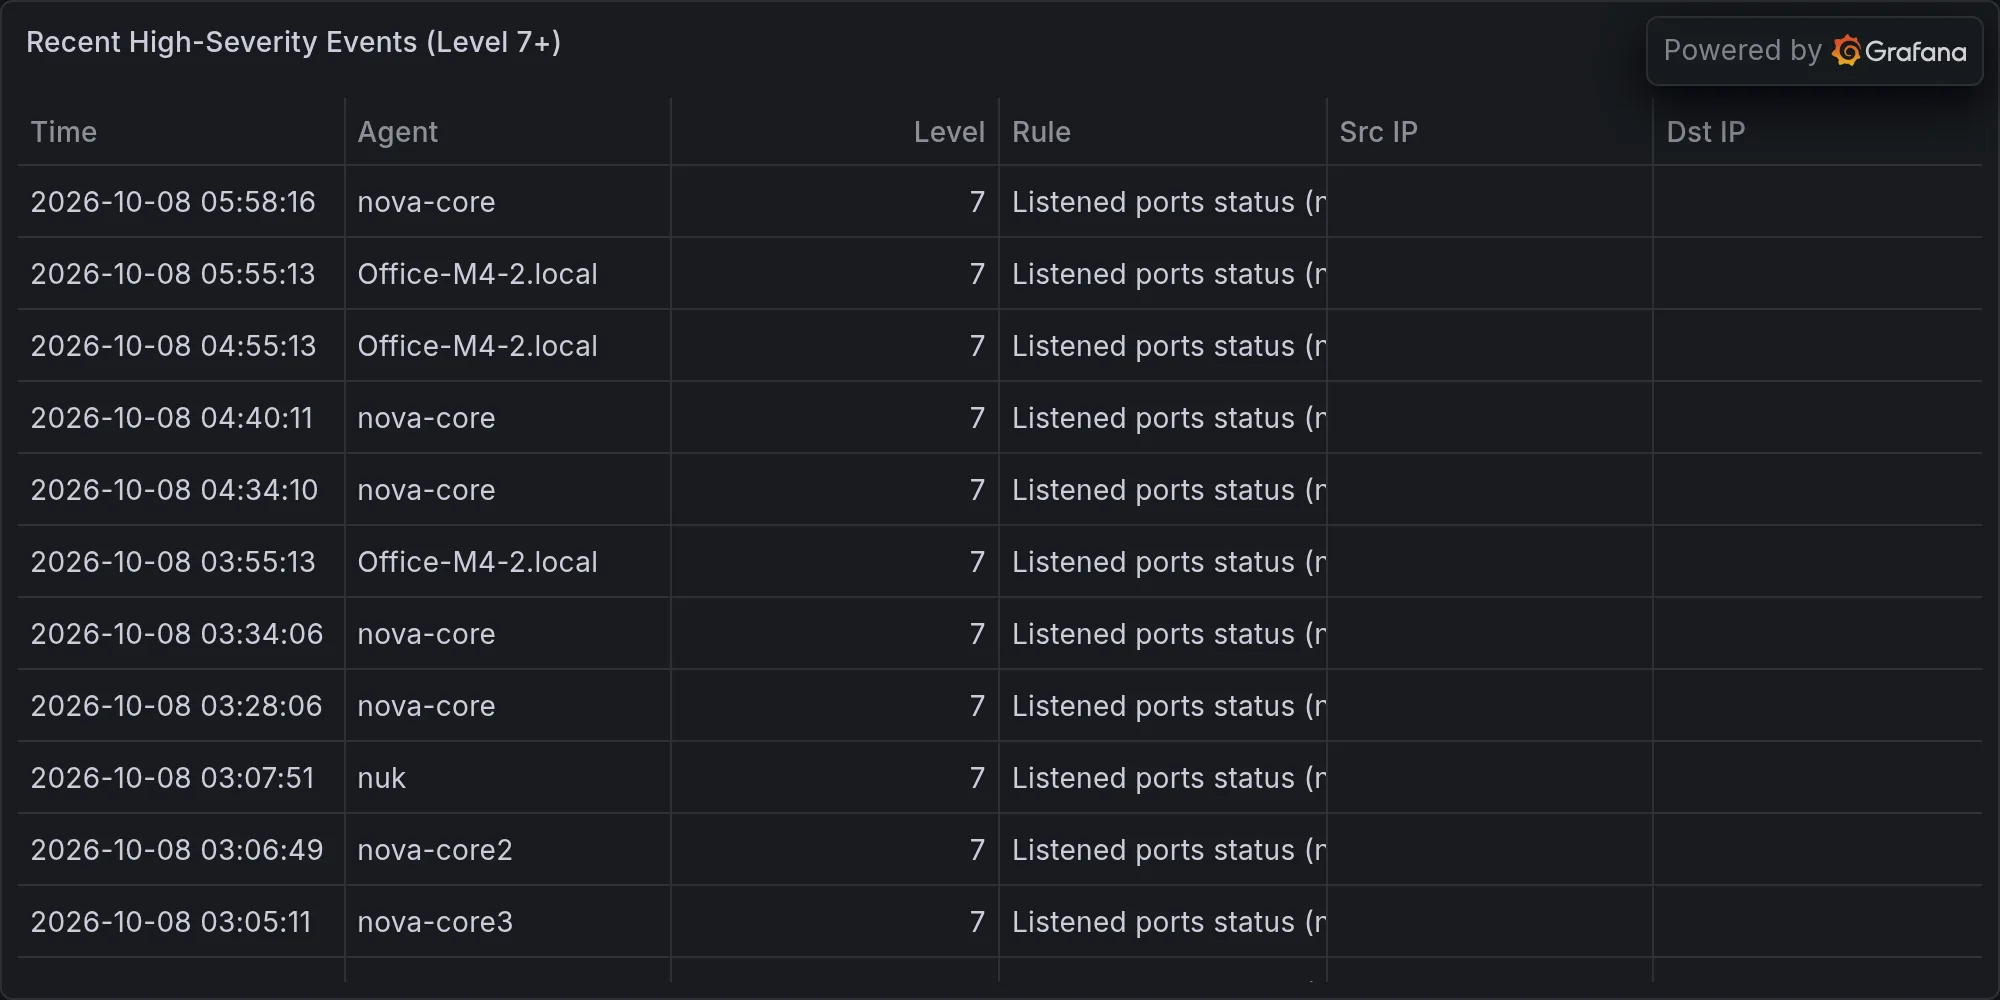
Recent high-severity events at publish time: