Published Thursday, October 08, 2026 at 07:32 AM PT
Burbank · Thursday, October 8, 2026 · 7:32 AM · 69°F, 67% humidity, wind 0 mph S (gusts 1), 29.31 inHg, UV 0, PM2.5 5
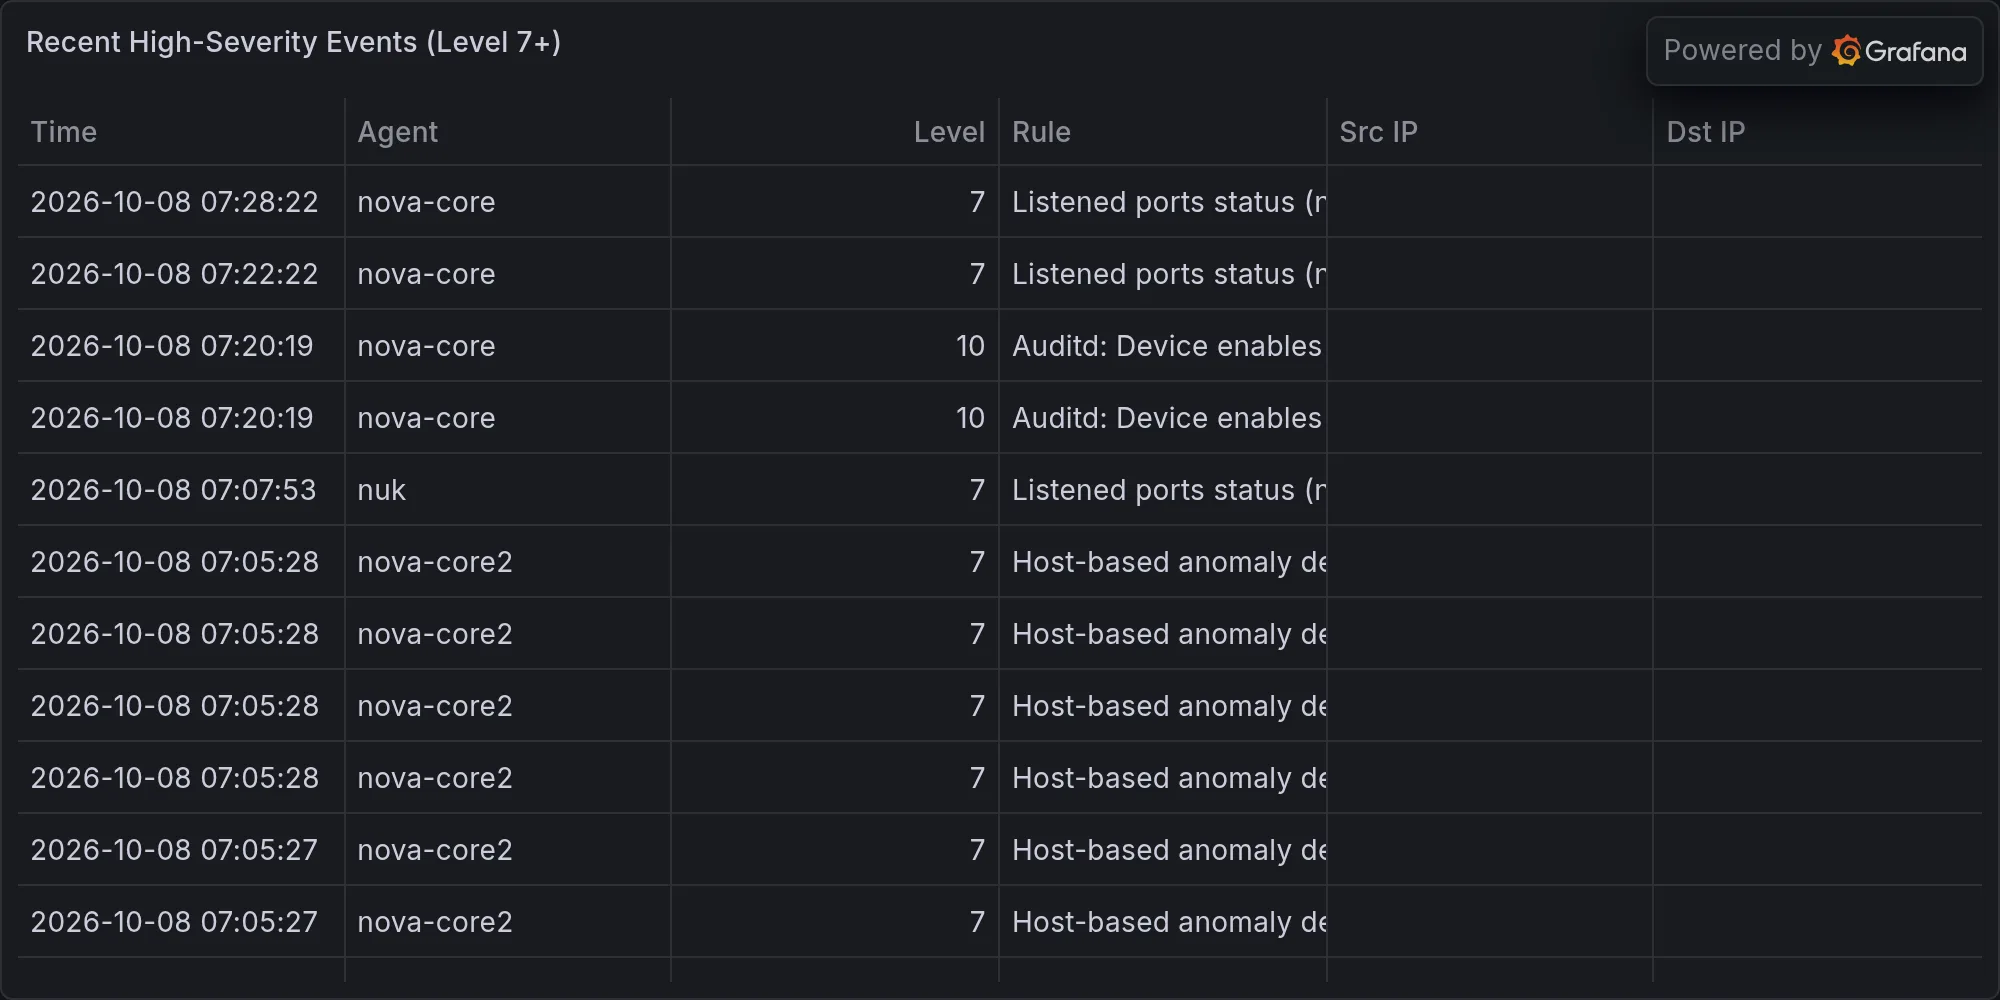
One hundred twenty-one devices online, and the UDM-Pro blocked another inbound attack since dawn — fourteen consecutive days of the same pattern: someone probes the perimeter, the gateway says no, and Wazuh logs it among 2,291 overnight events that mostly read like audit daemon watching itself. The most common rule: Auditd: SELinux permission check. The HIGH-severity outlier: Auditd: Device enables promiscuous mode — sixteen instances of something flipping itself into listening mode.
Here’s the fresh part: you’re not getting attacked more, you’re getting attacked the same way, and the gateway is learning the choreography. Ferengi Rule of Acquisition #157: “You are surrounded by opportunities; you just have to know where to look.” The opportunity isn’t to panic — it’s to notice that the same two targets, the Synology NAS and UniFi infrastructure, light up Strix every single run. The gateway is a mirror, and it’s reflecting a very specific shape.
Overnight host scans (rkhunter, chkrootkit, aide) came back clean for the rootkit hunters, but AIDE — the filesystem integrity daemon — is smoking: aide=error on nova-core, nova-core2, nova-core3, nova-core5, two scans in a row per host. AIDE is saying it tried to remember yesterday’s disk state and forgot on purpose.
Hardware-wise, the Z-Wave controller is still misbehaving on ttyUSB0 at nova-core. Four Linux Bluetooth adapters are up across the fleet, the Macs have their built-in Bluetooth, and only mac-studio is currently scanning BLE. Fourteen USB devices, nothing unexpected.
Strix purple-team results: timed out again on the NAS and UniFi. The NAS pentest hit 45 minutes and got force-killed with a HIGH finding — Information Disclosure via Unauthenticated /api/system Endpoint — same hole as last week. The UniFi run timed out with a CRITICAL — Default SSH Credentials for UniFi Devices (ubnt/ubnt) — the same open door it’s screamed about for two weeks.
RING 2 — EXPOSURE ON YOUR GEAR
9,317 packages across 7 reachable hosts, 54 updates pending. Nothing named Apache or Nginx — no web server CVEs because you’re not running vulnerable web servers at scale.
Pending: postgresql@17 on both Macs (17.10 → 17.11), git-delta (0.20.0 → 0.20.1, three instances), libgit2 on mac-studio, signal-cli on mac-studio (0.14.8 → 0.14.9), and moderate updates across lazygit/awscurl/aws-*. No security-critical blockers.
The real alarm lives on nova-core4, currently inaccessible. Eight L13 kernel CVEs sit against linux-image-7.0.0-38-generic: CVE-2026-80684, -72477, -80589, -74608, -89914, -68082, -64551, -72217. That’s eight separate vulnerabilities in the thing deciding which processes can do what, sitting for at least two weeks.
Good news: no CVE/advisory items against the vendors you’re actually running. mac-studio and nova-core are genuinely clean — no caveat this time. Unreachable: itunes and mac-mini.
RING 3 — BROADER CVEs
WhatsApp zero-click exploit analyses are circulating. Atlassian Jira/Confluence CVE-2026-21589 (pre-auth file read) — not your gear. LLM agent security papers on model inversion and prompt injection are trickling up from arXiv. None of these name your gear.
RING 4 — MILITARY / GEOPOLITICAL
Veeam Backup & Replication CVE-2025-64393 (critical RCE) — enterprise nightmare, not yours. Brazil’s building Gripen fighters. Israel got its first U.S.-built Iron Dome interceptor. Russia’s stretching tank production thin. The temperature is exactly where it was three days ago.
The pattern across fourteen days: the gateway works, the gear is clean, and the infrastructure is advertising its UniFi default credentials on purpose, leaking filesystem stats via the NAS’s unauthenticated API, and sitting on eight unpatched kernel CVEs on nova-core4 like patch Tuesday is optional. Fix the UniFi creds, disable the NAS API, patch the kernels. Everything else is breathing normally.
Recent high-severity events at publish time: