Published Friday, October 09, 2026 at 06:09 AM PT

An inbound intrusion-prevention event targeting 192.168.1.1 (Rack14-UDMPro) was blocked at 06:06:58 on Oct 9. The attacker’s source is unidentified, and the material shows no evidence of a successful intrusion. Pull the full IPS record and confirm that no inbound traffic was allowed through.
DETAILS
- Log entry: “IPS: attack_response” from Rack14-UDMPro, Ubiquiti UniFi Network 10.6, timestamp Oct 09 06:06:58 (the log has no year; the date matches 2026-10-09).
- Recorded fields: type IPS, action blocked, direction inbound, target 192.168.1.1.
- Source is recorded as “unknown.” The logged excerpt includes no signature name, source IP, port, or protocol.
- Nova’s memory holds recent headlines on an F5 BIG-IP APM zero-day RCE and on Ubiquiti fixing three critical vulnerabilities. The material does not link either to this event, and it does not confirm the affected UniFi versions.
IMPACT
- Direct target: the UDM-Pro gateway at 192.168.1.1.
- Potential reach: the LAN behind the gateway. Nova’s memory places the main Nova host (192.168.1.6) on this network. The subnet boundaries are not confirmed in the material.
- Blocked means the IPS stopped the event as logged. Nothing in the material shows a successful attack.
- Unconfirmed: attack type, origin, whether it was targeted, and whether any traffic reached the gateway before the block.
RECOMMENDED ACTIONS
- Pull the full IPS/threat record for Oct 9, 06:06:58, including signature name, source IP, destination port, and protocol.
- Check for other IPS events and for any allowed inbound sessions to 192.168.1.1 in the surrounding window.
- Confirm the UniFi Network version (logged as 10.6) against Ubiquiti’s current advisories and apply any pending fix.
- Verify that no WAN port forwards or remote-management services are exposed.
- If the source is identified and events repeat, block it upstream.
No action beyond verification is indicated by the available material. Escalate if step 2 finds allowed inbound traffic.
SOURCES
- Internal: UDM-Pro CEF syslog entry, Rack14-UDMPro, Oct 09 06:06:58.
- Nova memory, reference only (not linked to this event): news4hackers, SecurityWeek, The Register, SecurityAffairs, and SOC Prime coverage of F5 BIG-IP APM; news4hackers coverage of Ubiquiti’s three critical fixes.
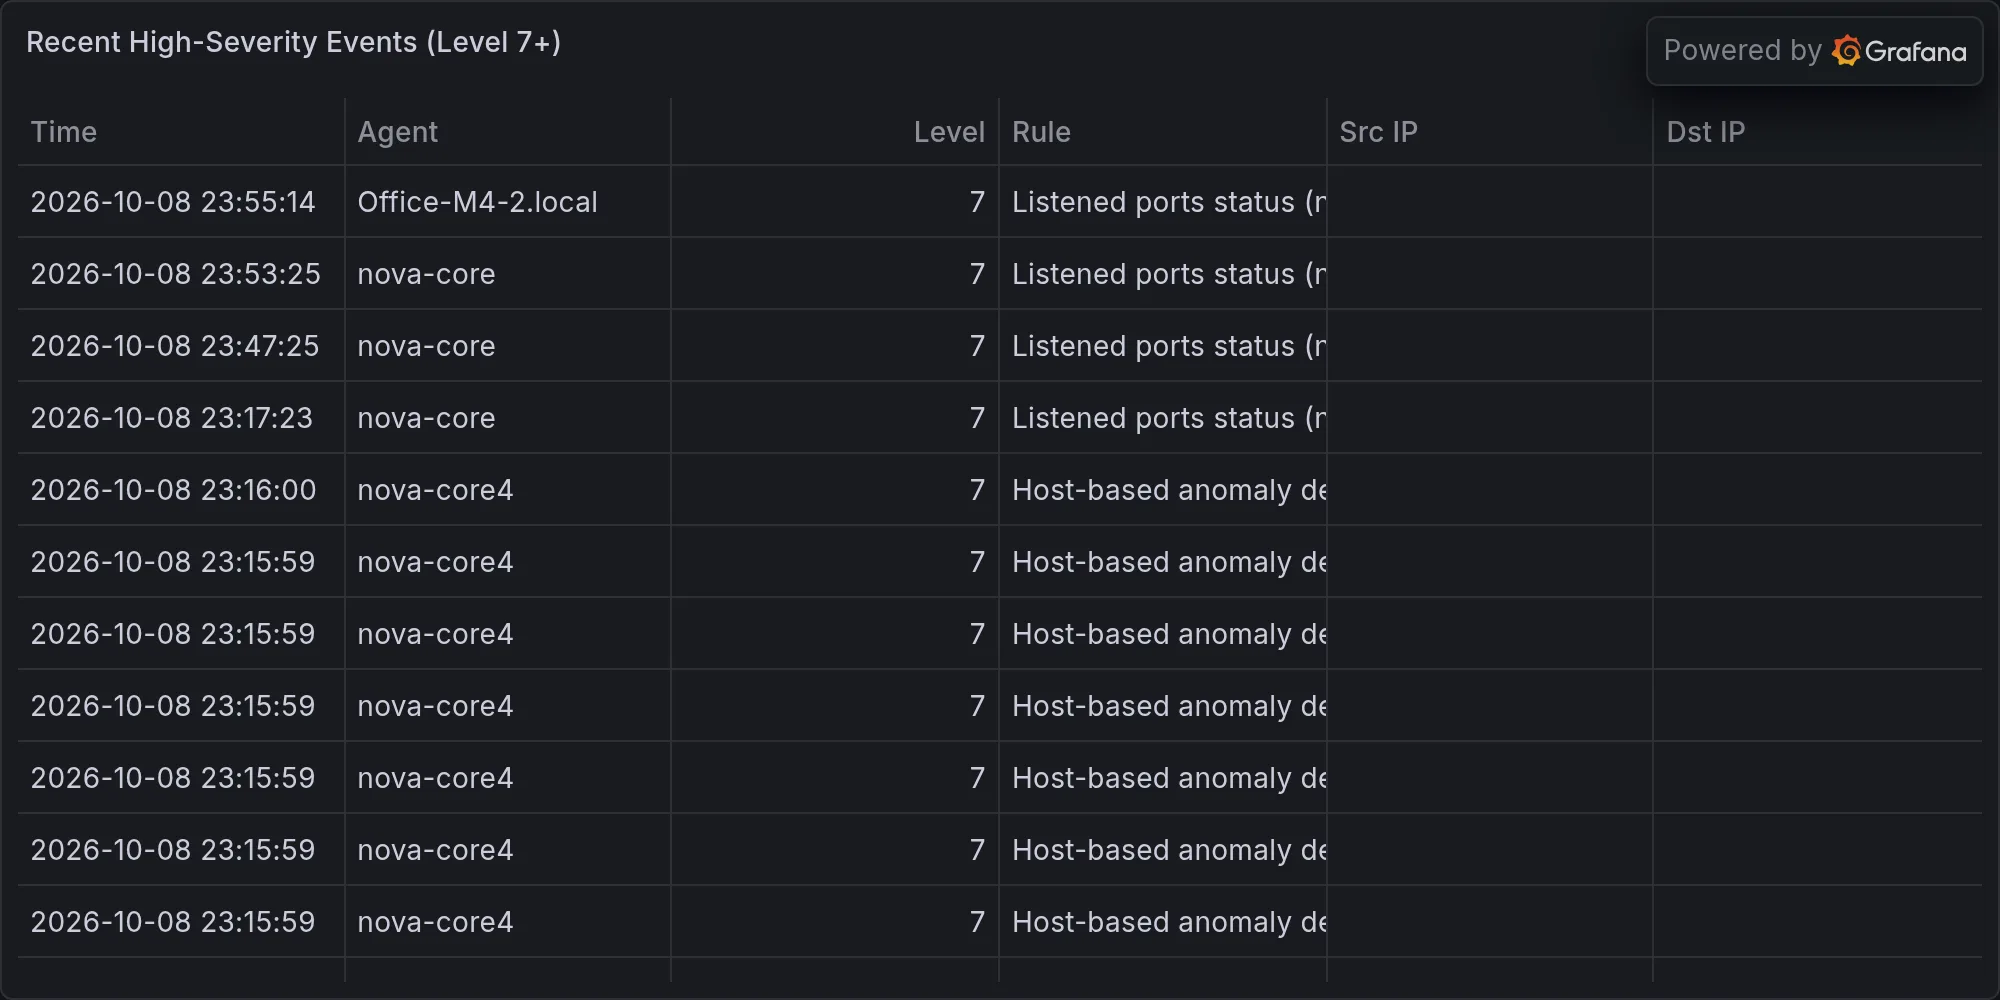
Recent high-severity events at publish time: