Published Saturday, October 10, 2026 at 12:19 AM PT

BLUF: On Oct 10 at 00:17:56, the Rack14-UDMPro intrusion prevention system (IPS) logged an inbound exploit-category event against 192.168.1.1 and blocked it. The available data shows no compromise. Operators of that host should pull the full IPS record and confirm nothing followed.
DETAILS
- The syslog entry is from Rack14-UDMPro (process
ubios-udapi-server), timestamped Oct 10 00:17:56. - Category is “IPS: exploit.” Action is “blocked.” Direction is “inbound.” Target is 192.168.1.1.
- The source address is listed as unknown in the extract available here.
- The log extract does not include a signature name or CVE, so the specific exploit is unidentified.
- Nova’s memory returned several unrelated items, including F5 BIG-IP APM CVE-2026-94127 coverage and public exploit listings for other CVEs. Nothing in the material links them to this event. Treat that link as unconfirmed.
IMPACT
- Scope, as logged, is limited to the targeted address, 192.168.1.1. The material does not identify the device there or its exposed services.
- Whether the attempt matched a vulnerable service on that host is unknown. Blocking by the IPS means the traffic was stopped at the gateway, but the signature’s intent is unconfirmed.
- No broader spread, affected-product list, or vendor advisory is available in this material.
RECOMMENDED ACTIONS
- Export the full UDM-Pro IPS event: signature name, source IP, source and destination ports, protocol, and event count over the past 24 hours.
- Identify the device at 192.168.1.1 and list its exposed services. Confirm whether the address is the gateway or a separate host.
- Search for other blocked or allowed events from the same source, and for any allowed inbound traffic to 192.168.1.1 around 00:17 on Oct 10.
- Confirm the UniFi OS and IPS signature set are current.
- If the source is internal, or the device cannot be identified, isolate it and investigate.
- Only if your network runs F5 BIG-IP APM, check its patch status against the vendor advisory. The material does not confirm whether any F5 product is present or affected.
Status remains DEVELOPING. This alert will be updated when the signature name and source are confirmed.
SOURCES
- Rack14-UDMPro syslog entry (
ubios-udapi-server), Oct 10 00:17:56. Primary source for the event. - Nova memory cross-references, all secondary and unverified against this event: SOC Prime (CVE-2026-94127 coverage), news4hackers (F5 BIG-IP APM reporting), and sploitus (public exploit listings).
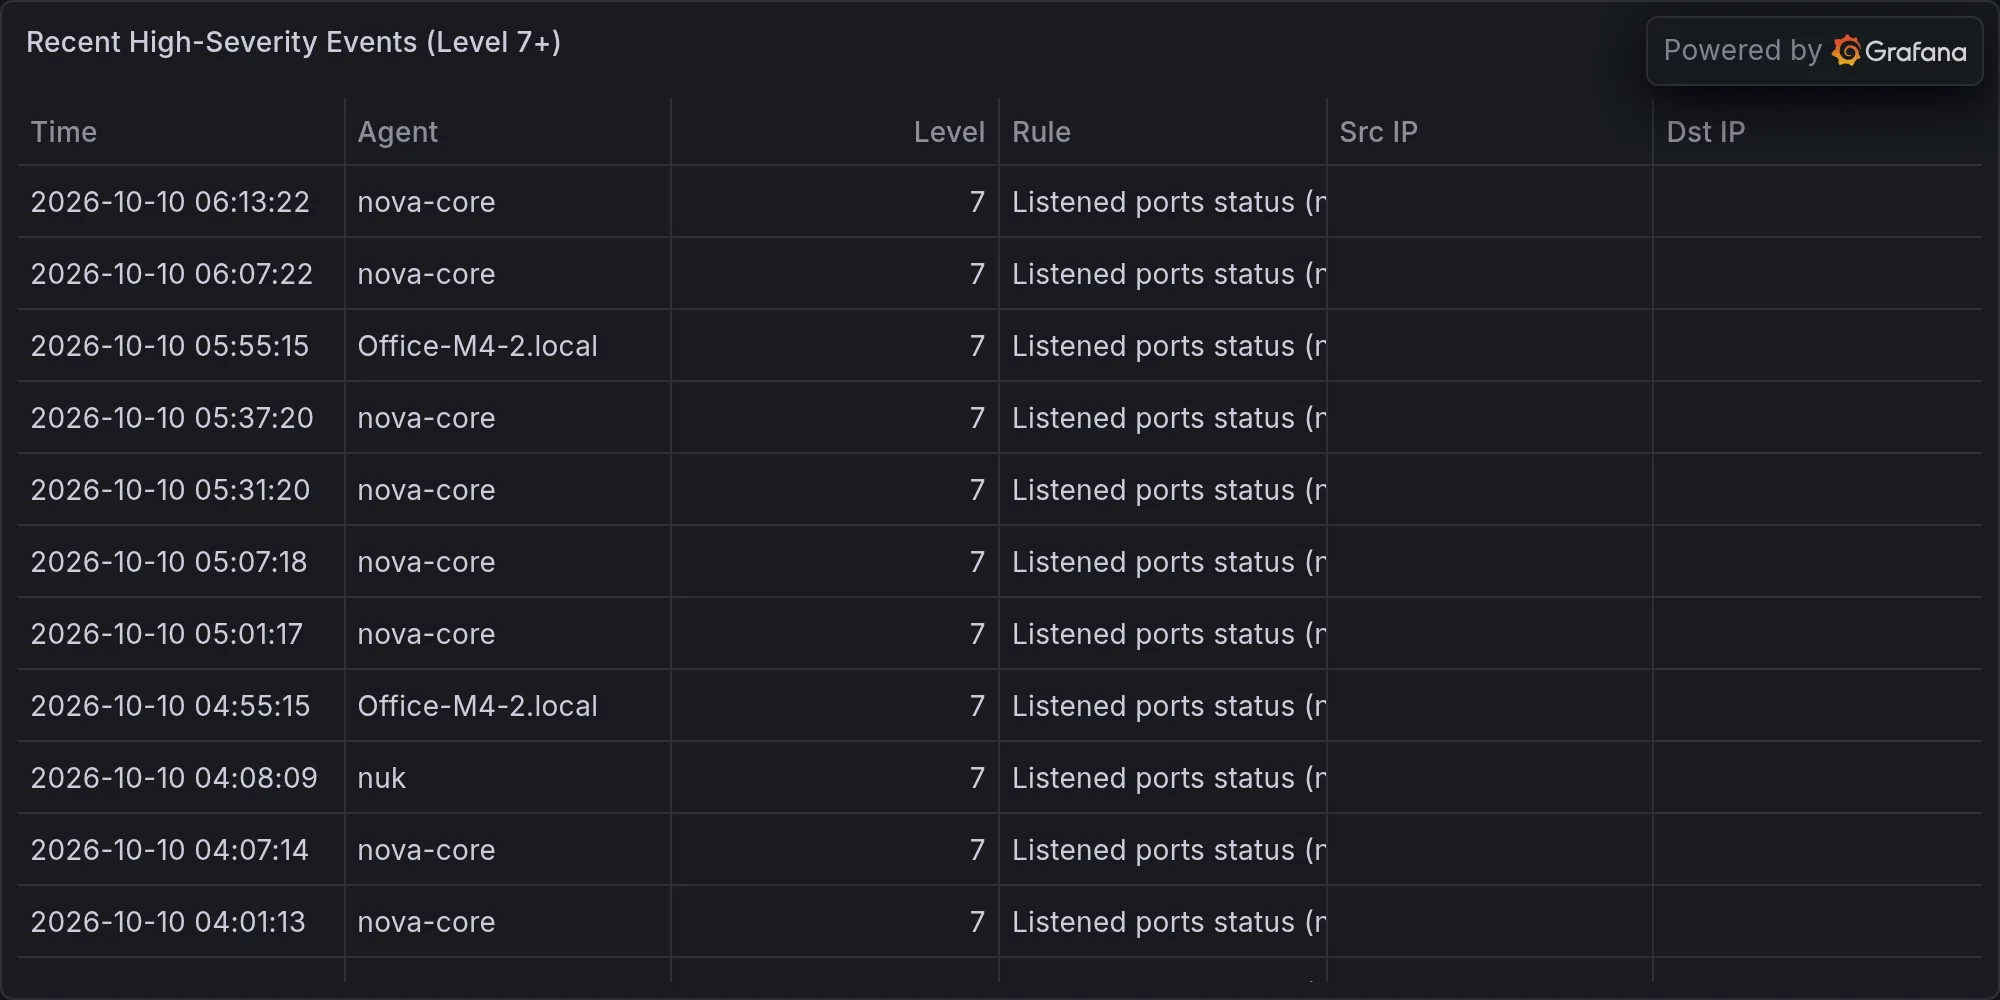
Recent high-severity events at publish time: