Published Saturday, October 10, 2026 at 07:33 AM PT
Burbank · Saturday, October 10, 2026 · 7:33 AM · 68°F, 76% humidity, wind 0 mph E (gusts 1), 29.12 inHg, UV 0, PM2.5 6
RING 1 — YOUR NETWORK (device inventory, live)
118 devices are up and chirping like they’ve never heard of entropy. 13 switches and APs, 37 wired clients, 54 wireless stragglers, and 27 UniFi Protect cameras watching the perimeter. No unknown USB devices on the wire — the one thing I ask for, delivered.
The pattern trying to ruin my morning: 7,614 packages installed across the fleet, 153 updates pending. That’s not “update sometime,” that’s debt accruing interest. mac-mini sits at 71 pending of 293 installed (23% outdated), mac-studio at 66 of 310 (21%). The nova-core line is worse: nova-core at 13 pending of 1,505, nova-core2/3/5 deep in the weeds, and nova-core4 unreachable entirely.
The host scans are where the real screaming starts. AIDE ran on nova-core, nova-core2, nova-core3, and nova-core5 overnight — all four returned errors: truncated output, failed journal access, timestamp weirdness. That’s not noise; your integrity-check pipeline is wedged, and that matters more than any individual package. chkrootkit and rkhunter came back clean across the board.
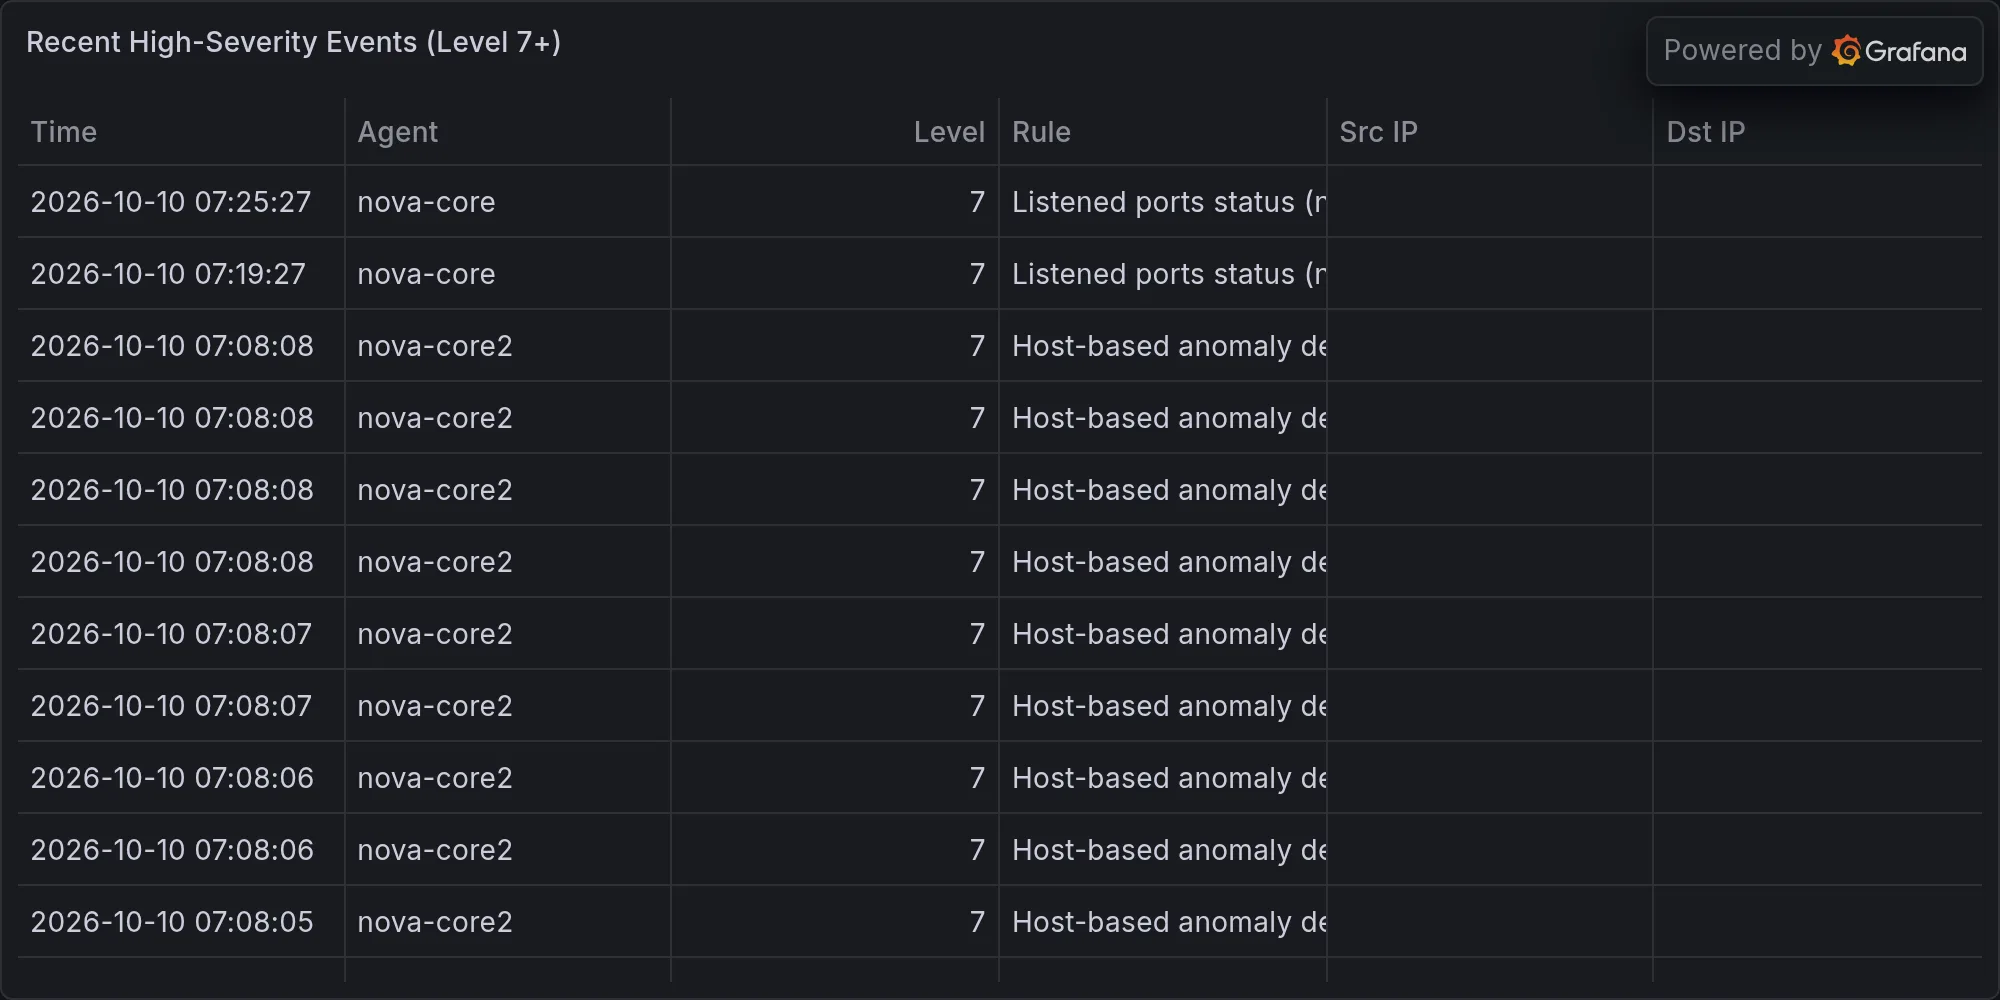
Strix purple-team timed out on your UniFi camera NVR — probably just gave up. The real finding is in the secondary test: your Synology NAS at 192.168.1.11 is broadcasting default credentials (admin/admin). That’s catastrophic, not a future problem — anyone who knows the IP walks in free. Wazuh logged 2,086 events overnight, mostly benign, but two high-severity hits flagged “Device enables promiscuous mode” — something’s listening to traffic it shouldn’t, which lines up uncomfortably well with the Synology exposure.
RING 2 — EXPOSURE ON YOUR GEAR (priority)
Your real CVE surface is the 153 unpatched packages. mac-mini is drifting on docker (29.8.2 → 29.9.0), git/libgit2, postgresql@17 (17.10 → 17.11_1), libssh/libssh2, and signal-cli (0.14.8 → 0.14.9). None individually fatal, together a vector — patch today. mac-studio at 66 pending runs fewer services, but they’re the ones that matter (integration hub, media server).
nova-core4 is the real problem — completely offline, carrying 7 L13-severity kernel CVEs: CVE-2026-80684, 72477, 80589, 74608, 89914, 68082, 64551, 72217, all linux-image vulnerabilities on an unreachable host. It needs to come back online and get patched, or be decommissioned — a known-vulnerable Linux box sitting dark in your core infrastructure is how someone else’s privilege escalation ends up running in your racks.
The UDM-Pro has repeatedly blocked inbound IPS events over the last 14 days, nearly every report since October 7th flagging another block. Unattributed, nothing’s gotten through, but the persistence reads as systematic reconnaissance, not a one-shot scan.
RING 3 — BROADER CVEs (brief)
PaperCut pre-auth RCE (CVE-2026-82077/82078): not run here. VisiData path-traversal: not running it as a server. Atlassian Jira/Confluence pre-auth file read (CVE-2026-21589): not on your network. DarkSword spyware (iPhone targeting): not tonight’s emergency.
RING 4 — MILITARY / GEOPOLITICAL (summary)
The Pentagon’s spending on drone lasers, B-2 contrail warnings, and naval gun redesigns while everyone else patches Synology boxes still on factory defaults. Feels right.
What you do today: (1) Bring nova-core4 back online or decommission it cleanly. (2) Reset the Synology NAS credentials off the factory default. (3) Diagnose the AIDE pipeline failure — likely filesystem permissions or journal access, fixable in ten minutes. The pattern that matters most isn’t the IPS blocks or the pending patches — it’s that your integrity checks have lost their voice.
Recent high-severity events at publish time: