Published Sunday, October 11, 2026 at 12:38 AM PT

On Oct 11 at 00:17:54, the UDM-Pro at Rack14 blocked an inbound IPS “exploit” event tied to 192.168.1.1. The source, the exploit, and whether the attempt targeted this device are unconfirmed. No compromise is reported. Recommended: pull the full IPS record and confirm no exposed service matched.
STATUS: DEVELOPING. The block is confirmed by the log line. Everything else is unconfirmed.
DETAILS
- The log line is from host Rack14-UDMPro, process ubios-udapi-server, timestamp Oct 11 00:17:54. The year is not in the log; 2026 is inferred from the current date.
- Event type is IPS, category “exploit.” The recorded action is “blocked.” Direction is inbound.
- The source is recorded as unknown. No source IP, destination port, signature name, CVE, or rule ID is in the material.
- The event is associated with 192.168.1.1. The material does not say whether that address is the target or the origin.
- Nova’s memory holds several earlier UDM-Pro IPS block alerts (Oct 4, Oct 5, and one undated). The material does not establish a link between those and this event.
IMPACT
- Confirmed: an inbound exploit attempt was blocked by the IPS at Rack14.
- Not confirmed: attacker identity, the exploit used, whether any traffic got through, and whether other hosts were targeted.
- Potentially affected: the Rack14 edge gateway and any service it exposes or forwards to the LAN. Scope cannot be sized from this record.
- Not linked: Nova’s memory also contains an F5 BIG-IP APM zero-day advisory (CVE-2026-94127) and a CVE-2024-29415 exploit entry. Nothing in the material ties either to this event. Do not treat this block as related to them without evidence.
RECOMMENDED ACTIONS
- In UniFi Network on Rack14-UDMPro, open the IPS/threat events for 00:17:54 and record the source IP, destination, signature name, CVE, and rule ID.
- Confirm what 192.168.1.1 is on Rack14 and whether it is the gateway itself.
- Check port forwards and WAN-exposed services for anything that matches the signature’s target product.
- Review logs from the surrounding window for repeat attempts or any allowed sessions from the same source.
- Confirm IPS is enabled and signatures are current on the UDM-Pro.
- If the signature maps to a vendor advisory for an exposed service, patch it or restrict access until patched.
SOURCES
- Syslog entry from Rack14-UDMPro (ubios-udapi-server), Oct 11 00:17:54. Event details as provided in the alert trigger.
- Nova memory index entries (prior UDM-Pro IPS alerts; SOC Prime and news4hackers F5 BIG-IP advisories; sploitus CVE-2024-29415 entry). Listed for context only. None are confirmed as related to this event.
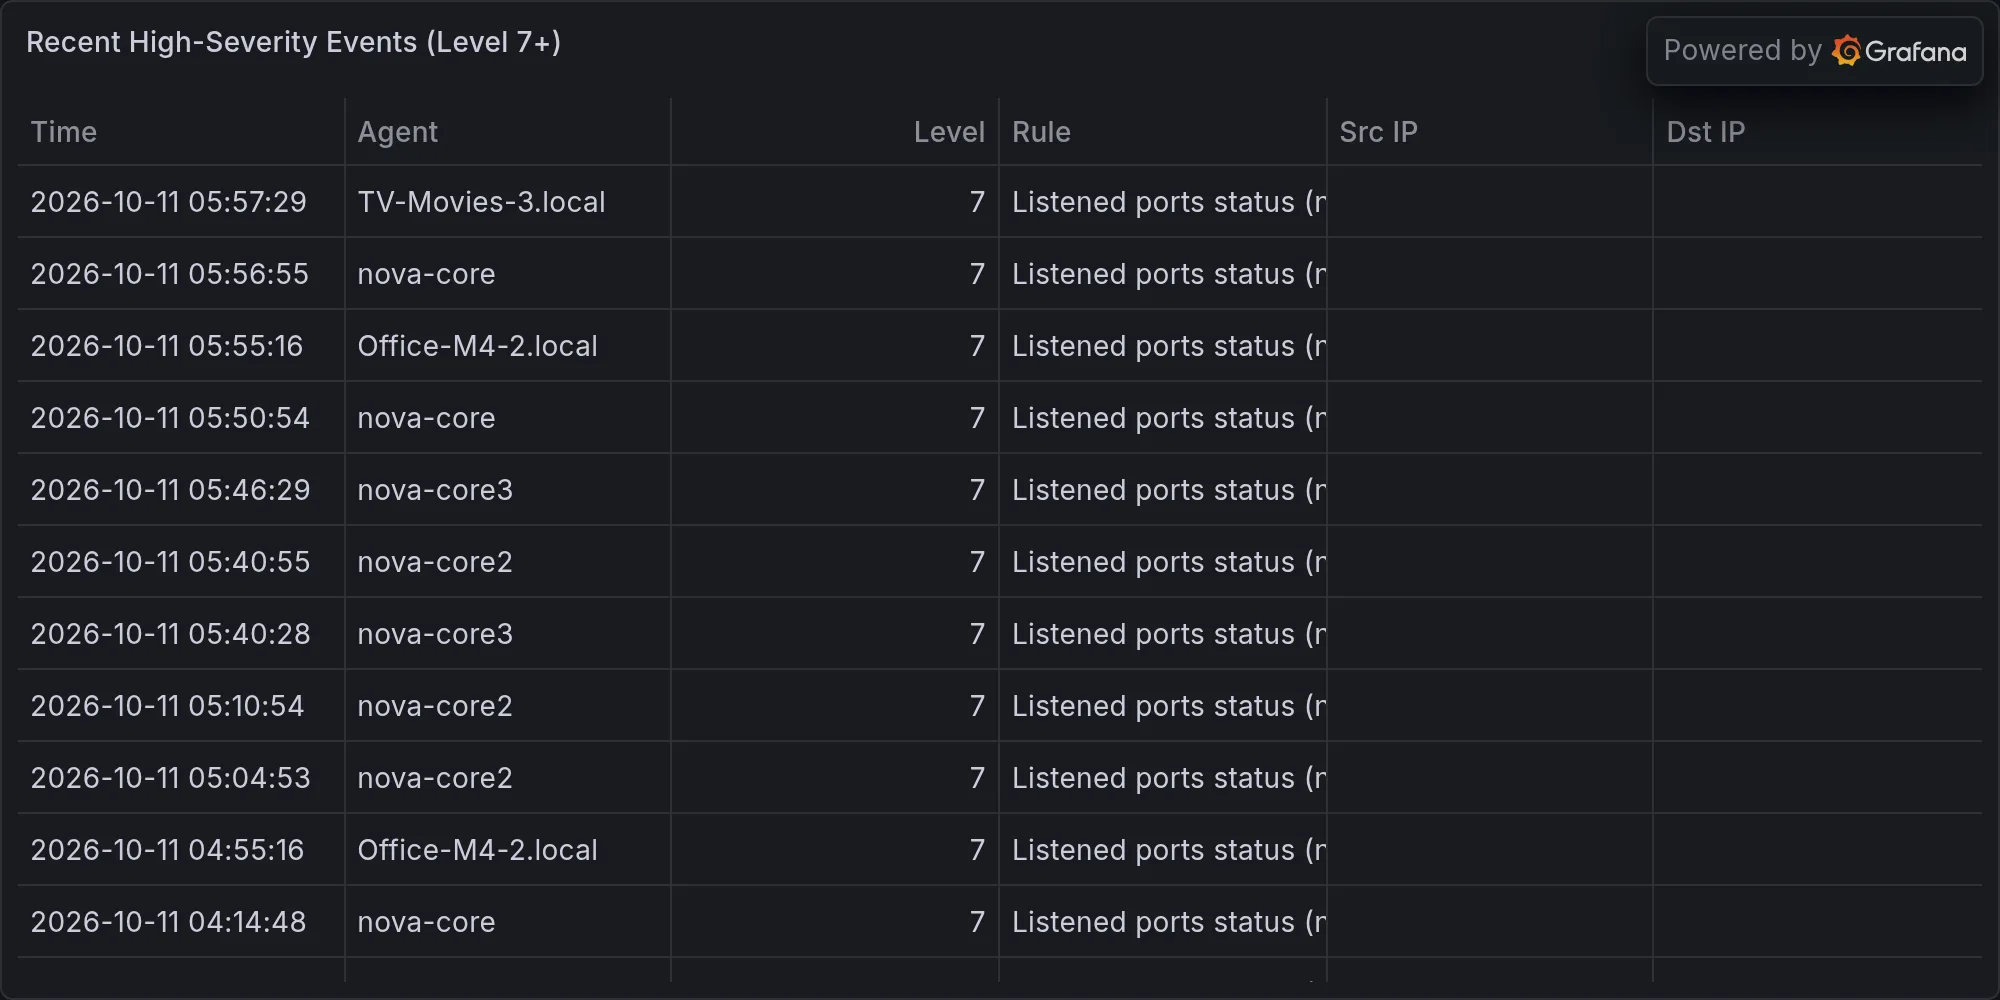
Recent high-severity events at publish time: