Published Sunday, October 11, 2026 at 12:18 PM PT

At 12:16:48 on Oct 11, the IPS on the Rack14 UDM-Pro blocked an inbound threat targeting 192.168.1.1. The attacker’s source, the threat’s name, and the targeted service are not in the available log, and no compromise is indicated. Status: DEVELOPING, monitoring.
DETAILS
- The log is a UniFi Network 10.6 CEF record from host Rack14-UDMPro, timestamped Oct 11 12:16:48.
- Event type is “ips”, action is “blocked”, and direction is “inbound.”
- Source is listed as unknown. The excerpt contains no source IP, source port, or signature name.
- The record is truncated after the product and version fields, so the signature ID and any destination detail are unavailable.
IMPACT
- Per the log, the IPS dropped the traffic. The excerpt shows no evidence of successful exploitation, but that is not confirmed either way.
- Scope is one gateway at Rack14, based on this record alone. Other devices are not assessed.
- Attribution is unconfirmed. Nova’s memory index holds prior headlines about blocked inbound events on this gateway (Oct 04, Oct 05, Oct 06) and a “zero-day campaign” headline. Their source material was not available for verification, so no link to this event is established.
RECOMMENDED ACTIONS
- Pull the full IPS event record from the UDM-Pro to get the source IP, port, and signature ID.
- Confirm the gateway firmware and UniFi Network application are current. Check Ubiquiti advisories against the signature once it is identified.
- Review port forwards, WAN-exposed services, and remote-access settings for anything unexpected.
- Check admin login history for sessions from unfamiliar addresses.
- If the source is identified as hostile or events repeat, escalate and consider blocking upstream.
SOURCES
- Primary: UDM-Pro CEF log record (Rack14-UDMPro), Oct 11 12:16:48.
- Secondary, unverified: Nova memory index headlines for related Oct 04–06 events and a multi-vector threat cluster. Excerpts only; not confirmed.
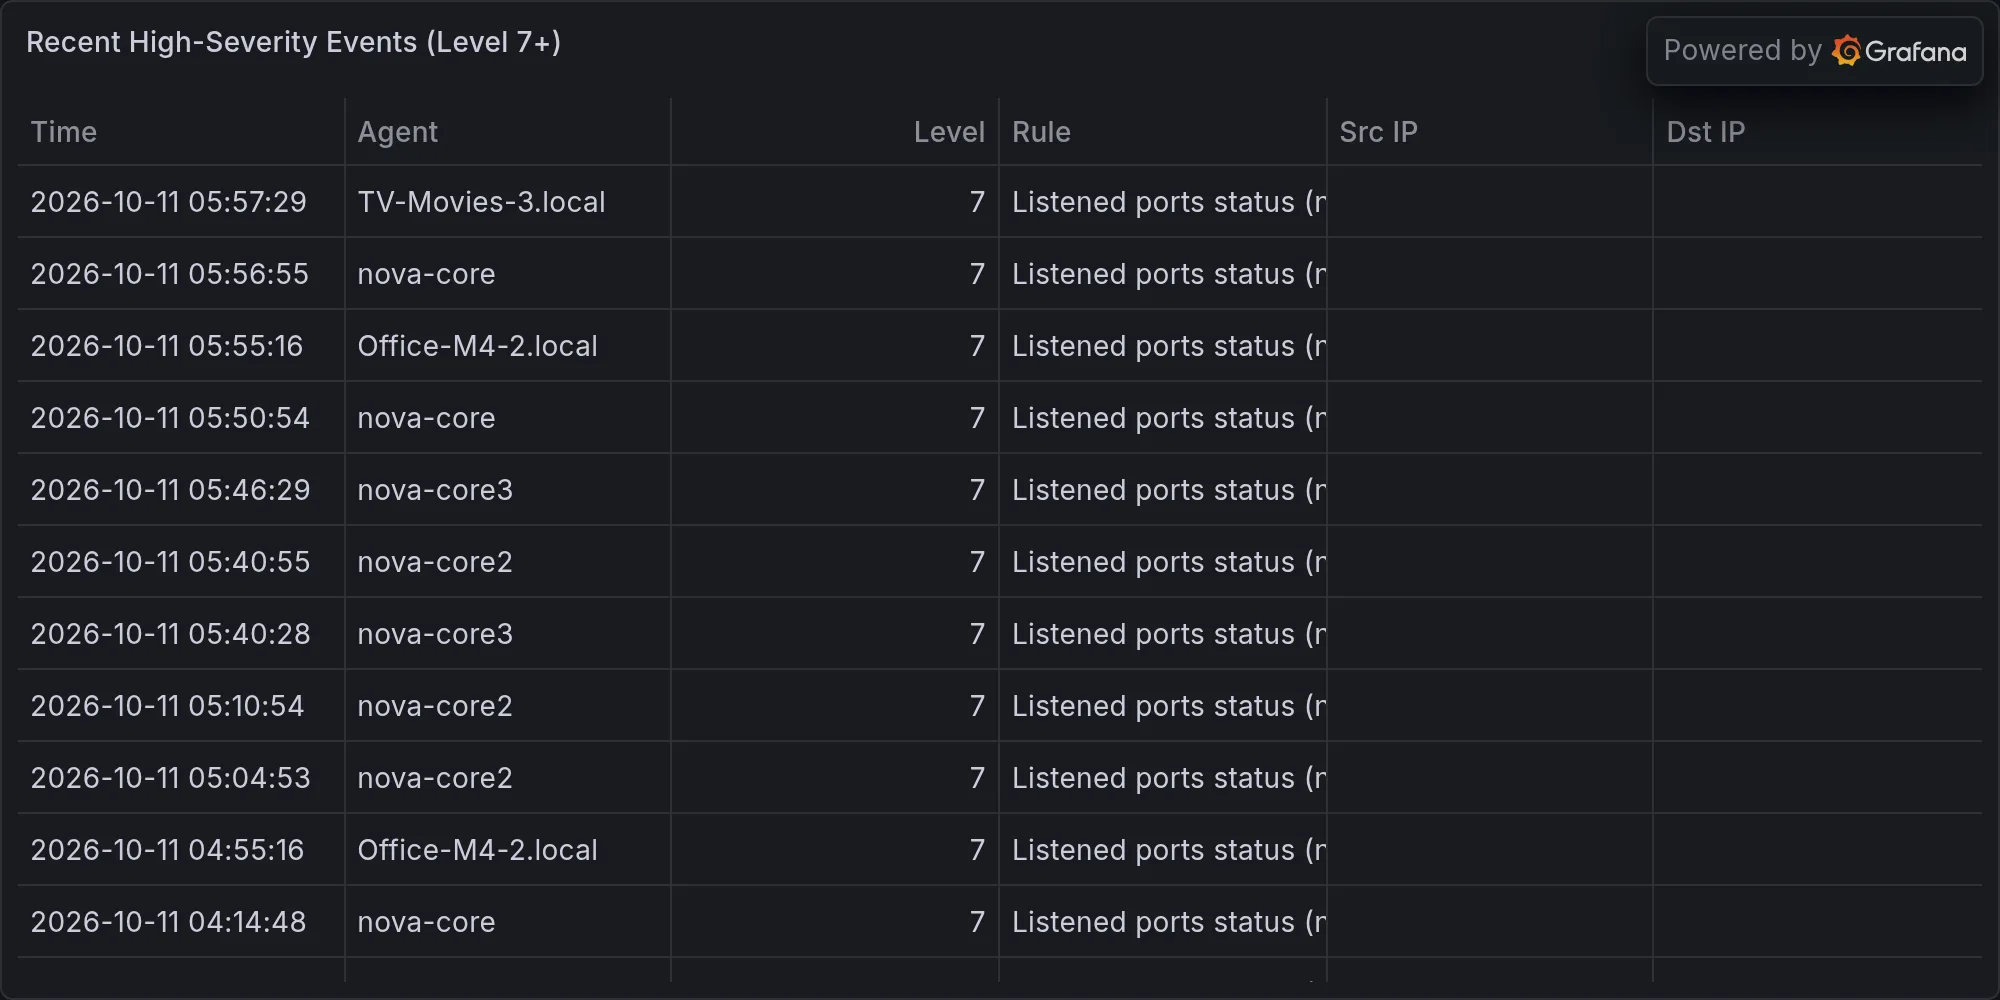
Recent high-severity events at publish time: