Published Monday, October 12, 2026 at 12:19 AM PT

An inbound exploit-class IPS event was blocked on the Rack14-UDMPro gateway at 192.168.1.1 on Oct 12 at 00:18:00. The attack source and exploit are unidentified, and nothing in the record shows a successful intrusion. No action is required beyond verification.
DETAILS
- The UDM-Pro logged an “IPS: exploit” event from host Rack14-UDMPro (process ubios-udapi-server[3415893]) at Oct 12 00:18:00. The log line omits the year.
- Recorded fields: type IPS, action blocked, direction inbound, source unknown.
- The threat is attributed to 192.168.1.1.
- The log line names no CVE, signature ID, or exploit family, so the specific exploit is unidentified.
IMPACT
- Scope is one event on one device. The supplied material contains no logs from other hosts and no record of other inbound attempts in the same window.
- Because the IPS action was “blocked,” this record does not indicate compromise. That conclusion depends on the blocked status shown in the log.
- Nova’s memory holds several earlier blocked inbound IPS alerts on the same UDM-Pro (Oct 4, 5, and 6). These are not confirmed as related to this event.
- Unconfirmed: one memory headline describes a “UBIQUITI ZERO-DAY CAMPAIGN.” It has no source link or CVE in the supplied material, so it is not established. A separate SOC Prime item concerns an F5 BIG-IP APM vulnerability, a different vendor, and is not linked to this event.
RECOMMENDED ACTIONS
- Pull the full UniFi IPS/threat log entry for Oct 12 00:18:00 to get the signature ID, category, and source IP. The current summary lists the source as unknown.
- Confirm whether 192.168.1.1 is the gateway’s own address and whether any port forwards or WAN-exposed services point to it.
- Check for any allowed (not blocked) inbound IPS events in the same time window.
- Confirm the UniFi OS and UDM-Pro firmware are current.
- Update this alert once the signature or source is identified.
SOURCES
- Syslog entry from Rack14-UDMPro (ubios-udapi-server[3415893]), Oct 12 00:18:00.
- Nova memory entries: prior UDM-Pro IPS alerts (Oct 4, 5, and 6), a “Ubiquiti zero-day campaign” headline (unverified), and a SOC Prime F5 advisory (unrelated vendor).
- No external advisory or signature match was available to confirm the event type or attribution.
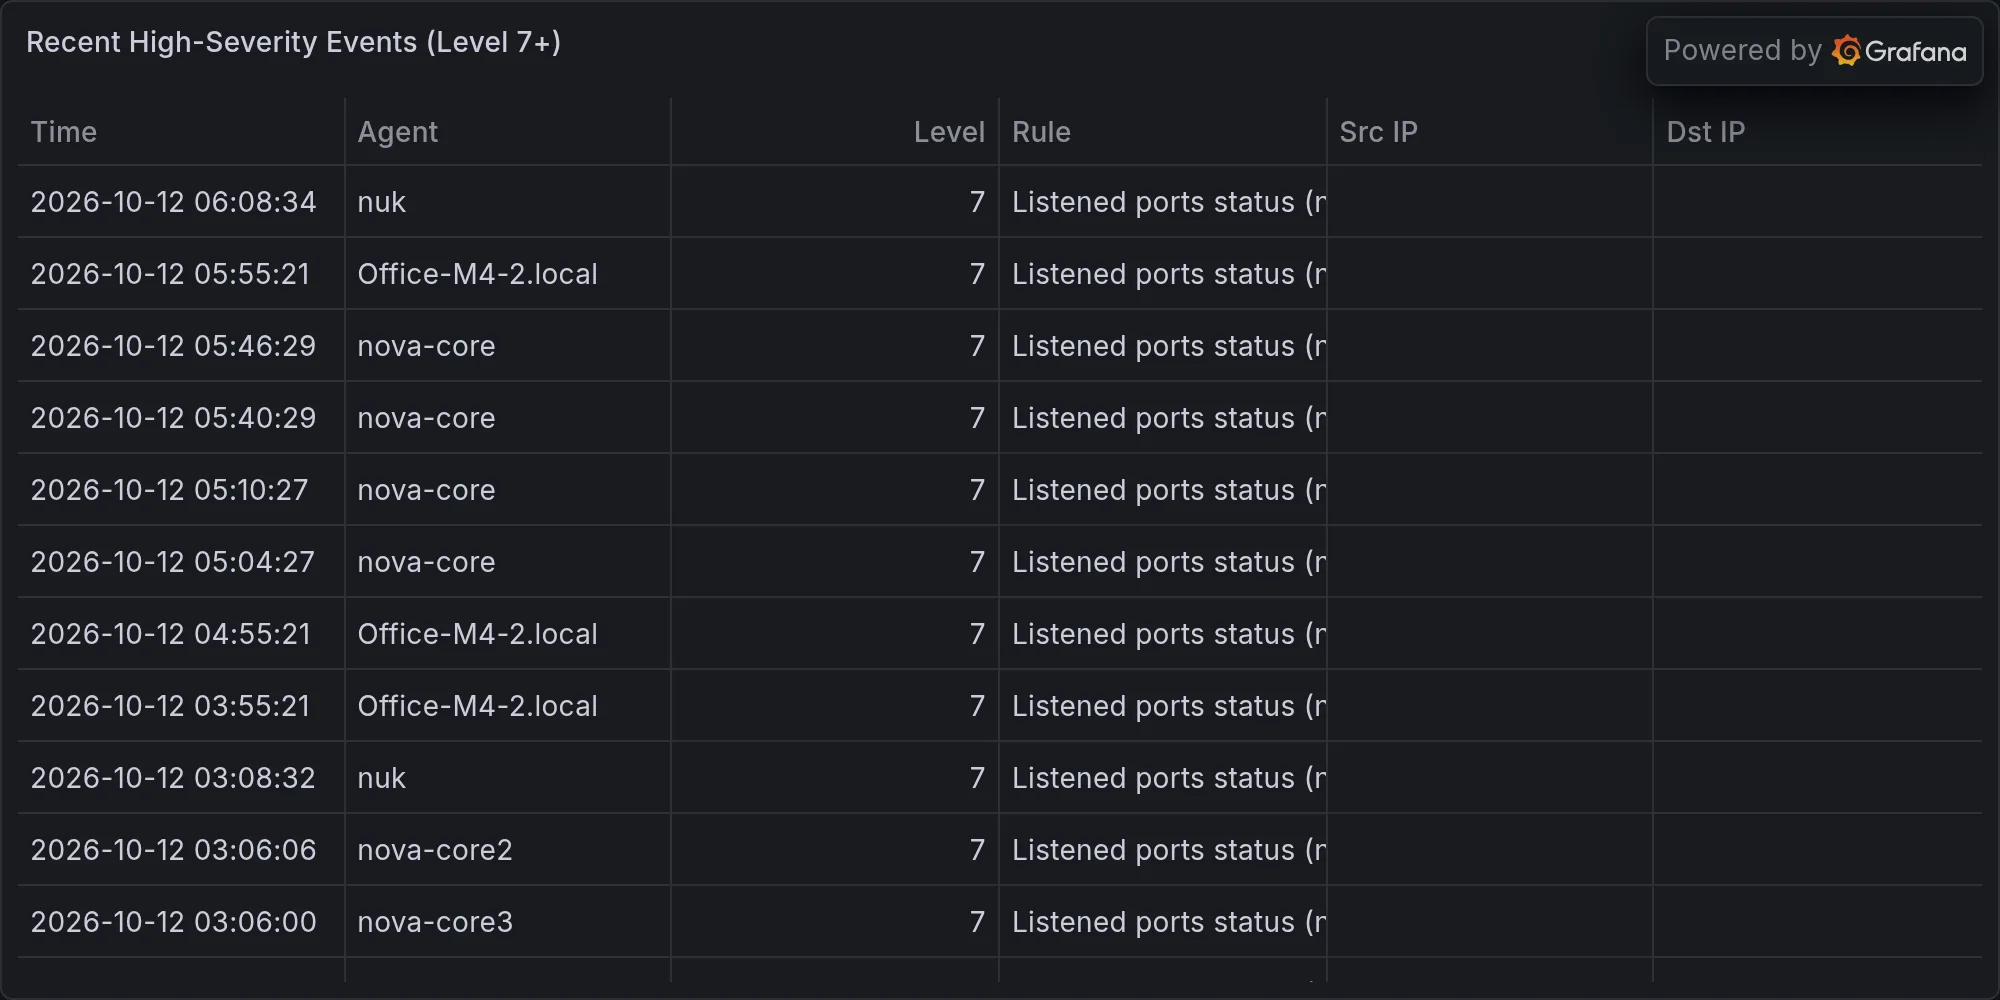
Recent high-severity events at publish time: