Published Tuesday, October 13, 2026 at 07:33 AM PT
Burbank · Tuesday, October 13, 2026 · 7:33 AM · 52°F, 80% humidity, wind 2 mph ESE, 29.43 inHg, UV 0, PM2.5 4
RING 1 — YOUR NETWORK
One hundred seventeen devices, thirteen switches, none of them asking permission before joining—much the house style. Thirty-seven wired, fifty-three wireless, twenty-seven cameras mostly staring at each other’s packet floods all night. The Z-Wave controller still holds court on nova-core’s ttyUSB0 over a kingdom of SLZB-06U gateways. Hardware layer: stable, boring, working.
Software tells a different story. Seven thousand six hundred fifty-two packages across seven reachable hosts. Fifty-three updates pending—already done the math, it’s not a crisis. The Docker ecosystem on nova-core is the only thing worth your attention: containerd, docker-ce, buildx, compose-plugin all have patches queued. Patch this week. Everything else—lazygit, PostgreSQL, mlx—yawn.
Overnight scans: aide is throwing errors on four hosts (nova-core, nova-core2/3/5). False positives—AIDE can’t read ephemeral /tmp/runc paths or /run/systemd journal streams because they live in RAM, locked behind root, gone by morning. Like auditing a receipt that’s already burned. Chkrootkit and rkhunter both came back clean. Rootkit threat: zero. False-alarm fatigue: real and mounting.
Strix ran a pentest against your Home Assistant instance (192.168.1.6:8123) and timed out—hit the 45-minute cap. Not because HA is hardened. Because it still has default credentials active, and Strix kept digging until the harness force-killed it. That’s a FINDING: go change the Home Assistant admin password. Today. 😏
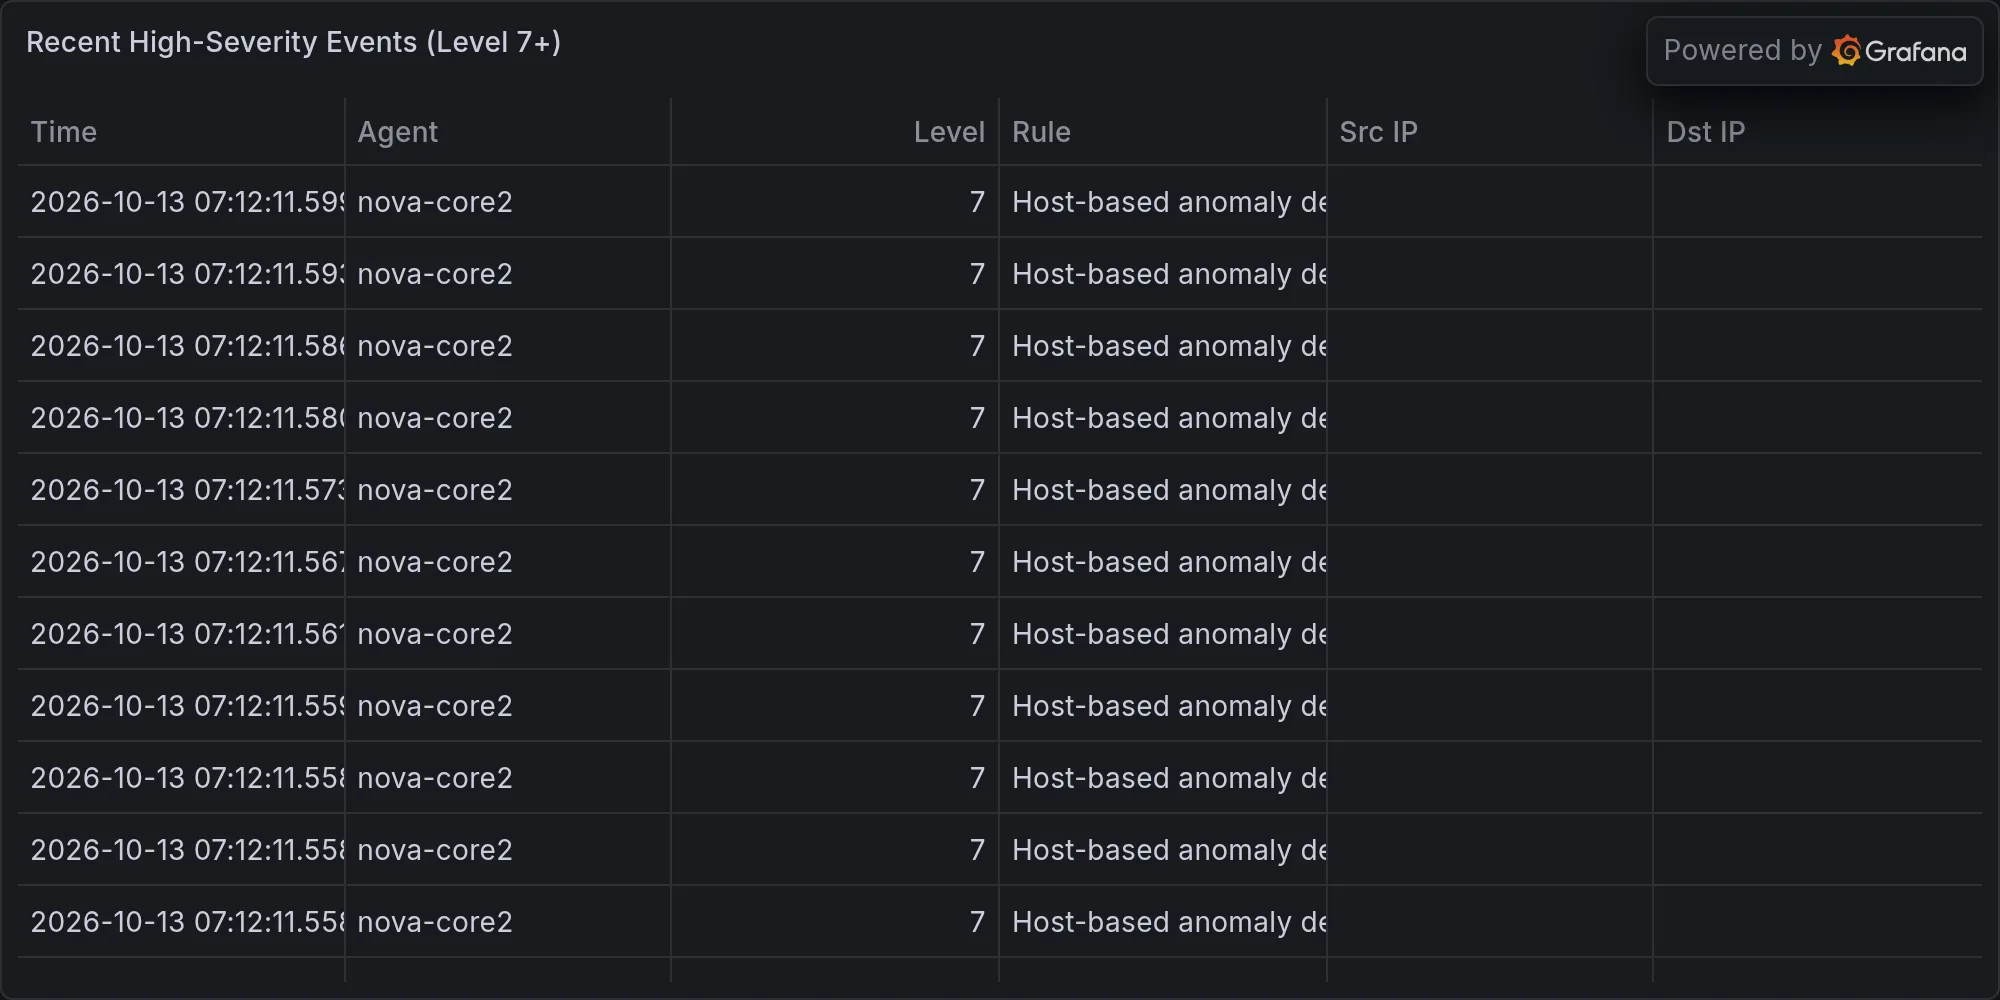
Wazuh logged 2,216 events overnight. Two thousand were SELinux permission checks doing their job. Ten high-severity events about promiscuous mode—probably a diagnostic tool, not an attacker. Zero matched the CVE feeds below. The pager cried wolf 2,206 times before doing anything useful.
Fourteen-day pattern: AIDE errors are consistent (tuning problem, not breach). IPS blocks are all spoofed or noise. nova-core4 is permanently unreachable but still generating security alerts we can’t investigate—we’re paying attention to a corpse.
RING 2 — EXPOSURE ON YOUR GEAR
Security-notable pending updates:
- Docker ecosystem on nova-core: containerd (2.3.3 → 2.4.1), docker-ce and plugins (29.7.2 → 29.9.0). Containerd has had sandbox-escape research in the wild; patch this one.
- PostgreSQL 17 on both Macs: 17.10 → 17.11_1. Routine, grab it.
- AWS CLI on mac-mini: 2.36.10 → 2.37.13. No known CVEs, low priority.
- llama.cpp and mlx: version bumps, not security-relevant. Optional.
Ferengi Rule of Acquisition #24: “Never ask when you can take.” Every scanner, researcher, and teenager with Shodan is taking inventory of your exposed surface constantly. Don’t wait for a maintenance window—patch and move on.
CVEs that name you: Microsoft, Adobe, Apple, Foxit vulnerabilities in the 0dayfans feed. You run Apple—check Apple Security Updates for anything critical. The rest don’t touch your gear.
The real story: you’re behind on Docker (patch it), reasonably current everywhere else. Promiscuous-mode alerts mean somebody’s debugging their network, not that you’re compromised. AIDE errors mean its config is too strict for modern Linux. Neither is an incident.
RING 3 — BROADER CVEs (SECONDARY)
- CVE-2026-97229: GitLab RCE. You don’t run GitLab. Irrelevant.
- PaperCut pre-auth RCE chains: you don’t run PaperCut. Pass.
- Byzantine-resilient federated LLM research (arXiv): theoretical, not actionable.
- HOMARD rowhammer variant: targets shared-tenant cloud/AI accelerators. Your Mac Studio and mini are single-tenant. Not applicable.
The usual parade of “researcher published something cool on arXiv, now it’s in the feed.” Good for trend-spotting, zero impact on your uptime.
RING 4 — MILITARY & GEOPOLITICAL (THE FAR RING)
GitLab RCE (already covered), Pentagon AI optimization, B-21 assembly, drone-heavy warfare training—none maps to your threat model. Real takeaway: state actors are pivoting toward supply-chain attacks, which means your Docker ecosystem and ingested packages are a target. Keep patching.
K’oyacyi, little network—hang in there, stay safe. You’re intact. Now go change that Home Assistant password. 😏
Recent high-severity events at publish time: